Tactics Techniques and Procedures TTP: A 2026 Guide
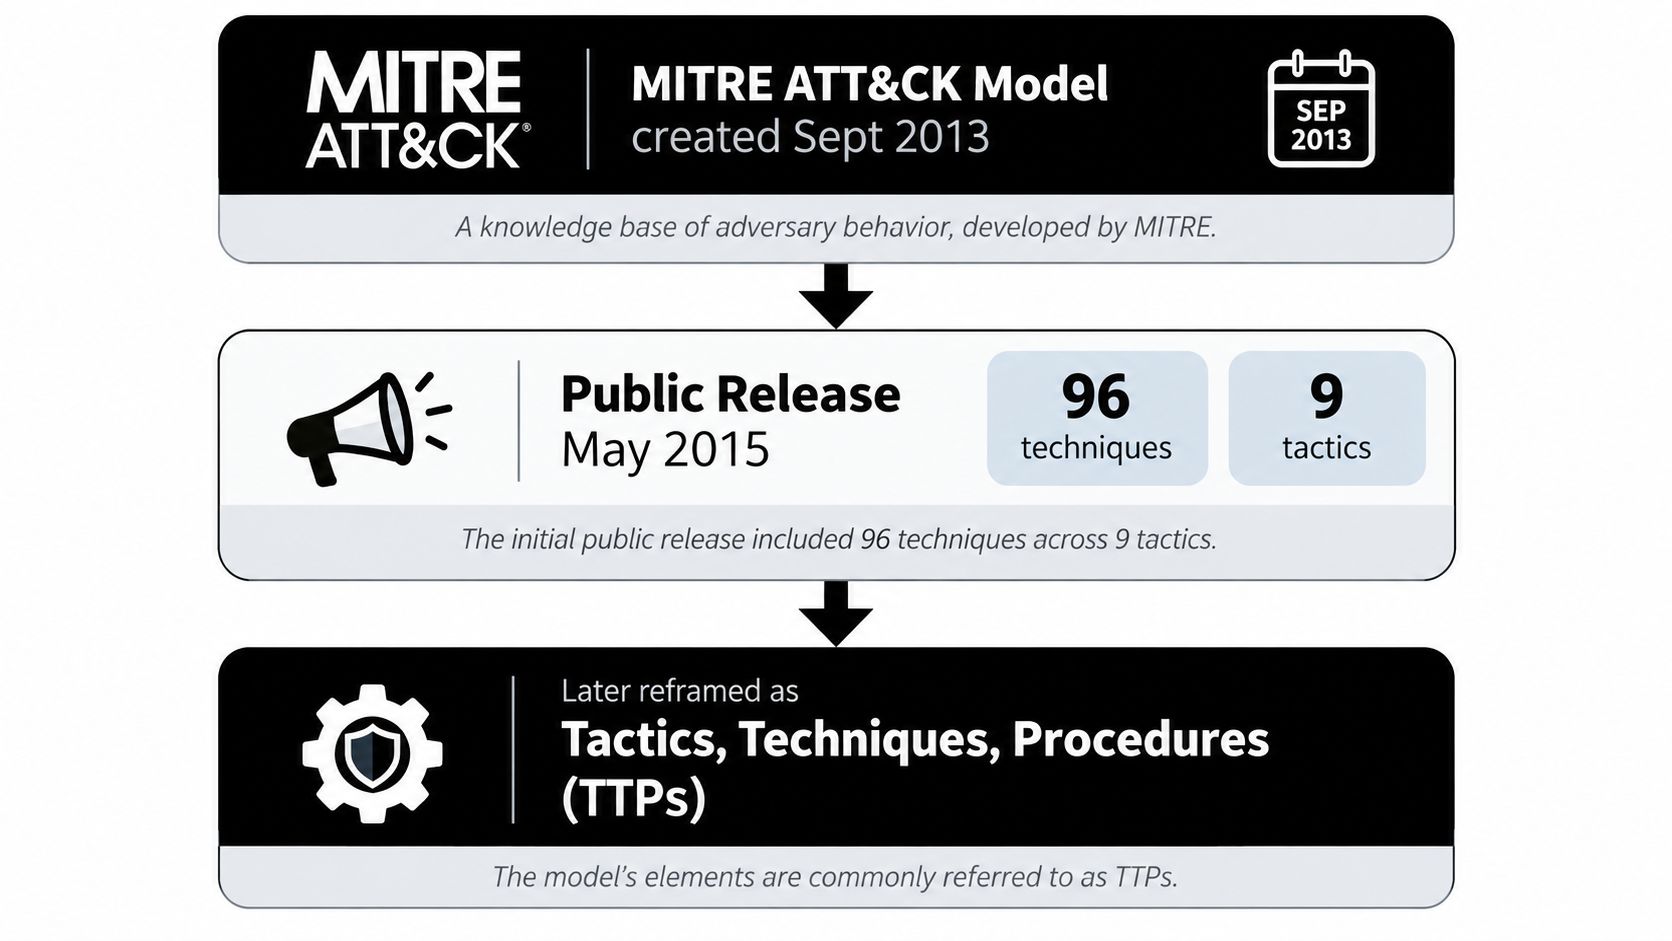
Tactics, techniques, and procedures form an adversary's behavioral vocabulary: tactics answer why, techniques answer how, and procedures capture the concrete implementation. MITRE built the initial ATT&CK model in September 2013, then released it publicly in May 2015, containing 96 techniques arranged under 9 tactics.
That origin matters because TTPs turn scattered security events into an operational modelA suspicious PowerShell process, an unusual cloud login, and a remote administrative connection are not just separate alerts. Combined, they may outline an attack path that a SIEM can detect, investigate, automate, and retain as compliance evidence.
Table of Contents
- What TTPs Really Mean in Modern Threat Defense
- TTPs Compared to IOCs and Other Indicators
- Mapping TTPs to the MITRE ATT&CK Matrix
- Under-Covered TTP Areas Worth Defending
- Hypothesis-Driven Hunting and SIEM Correlation Rules
- Operationalizing TTPs in a Unified SIEM, SOAR, and XDR
- Tuning, Triage, and Compliance Evidence on One Loop
What TTPs Really Mean in Modern Threat Defense
MITRE built ATT&CK to record common adversary behavior, especially the tactics, techniques, and procedures employed by advanced persistent threats. Since then, the framework has become a common language across threat intelligence, detection engineering, incident response, and security validation. MITRE's ATT&CK design and philosophy explains how techniques differ from procedures, where procedures are concrete, observed implementations of techniques.
The three layers defenders need to separate
Tactics describe what the adversary aims to achieve. Credential Access, for instance, indicates that the actor seeks authentication material.
Techniques describe the method employed to reach that objective. OS Credential Dumping is more specific than the broad tactic because it pinpoints the behavior defenders need to recognize.
Procedures describe the implementation tied to a specific actor or intrusion. MITRE's FAQ offers a concrete example: PowerShell can inject into lsass.exe and scrape LSASS memory to extract credentials. In that example, Credential Access is the tactic, OS Credential Dumping is the technique, and the particular PowerShell activity is the procedure. See MITRE's ATT&CK FAQ for the way the framework defines procedures.
That distinction affects how detection engineers author rules. A rule looking for one malicious script hash depends on a single artifact. A rule that detects a process accessing LSASS memory, particularly when correlated with suspicious PowerShell parentage and an unusual user context, states a behavioral hypothesis.
Practical rule: Map the event to the technique while retaining the procedure details. The technique provides the rule with a lasting category. The procedure shows what to search for, what to suppress, and which actor behaviors warrant escalation.
Indicators may expire quickly when attackers change payloads, infrastructure, and filenames. A mapped TTP stays useful far longer because the underlying behavior often remains even as the implementation shifts. When reading a threat report, pull out three answers: what objective was the actor pursuing, how did the actor pursue it, and what precise implementation appeared in the evidence?
That practice prevents TTPs from turning into decorative ATT&CK tags. It turns them into an operational vocabulary for SIEM rules, EDR investigations, XDR detections, and incident timelines.
TTPs Compared to IOCs and Other Indicators
Indicators of compromise are valuable, but they are not the same as TTPs. A file hash, domain, URL, or IP address points to an artifact. A TTP captures behavior that can repeat across different campaigns, malware families, accounts, and infrastructure.
An IOC is frequently most useful early in an investigation. A known hash can enable quick triage. A blocked domain can stop a connection. A suspicious URL can add context to an alert. However, atomic indicators are fragile by nature. After an attacker recompiles a payload, changes infrastructure, or relies on a legitimate service, the indicator may stop helping.
TTPs provide the durable detection layer:
- Atomic indicators support speed: Blocklists and enrichment systems can immediately act on known artifacts.
- Behavioral techniques support correlation: SIEM rules can merge process, identity, network, and cloud events into a pattern of attack.
- Procedures support precision: By reviewing parent process, account, target, timing, and surrounding activity, analysts can tell an expected administrative action apart from a suspicious implementation.
- Threat intelligence adds context: Indicators may increase confidence or help explain a technique, but they should not substitute for behavioral coverage.
A frequent failure mode is an indicator-only SOC that devotes its time to refreshing feeds and investigating isolated matches. This produces a whack-a-mole cycle. The team responds to what has already been identified rather than asking what an attacker must do to reach an objective.
| Dimension | TTPs (Behavioral) | IOCs (Atomic) |
|---|---|---|
| What they describe | Adversary objectives, methods, and implementations | Files, addresses, domains, URLs, and other artifacts |
| Primary use | Hunting, correlation, detection engineering, and attack-path analysis | Blocking, enrichment, and rapid triage |
| Durability | Usually survives changes to payloads and infrastructure | Can become obsolete when artifacts change |
| SIEM value | Connects events across data sources | Adds context to individual events |
| Main trade-off | Requires richer telemetry and careful tuning | Easier to deploy but narrower in scope |
Striking the right balance is essential. Experienced teams do not throw away IOCs. They apply them as enrichment within a detection model centered on TTPs. Organizations constructing that model might also require specialized skills in collection, actor tracking, and analysis, so finding threat intelligence talent can help when internal coverage is limited.
The practical position is straightforward: use IOCs for immediate signal, and use TTPs for lasting advantage. This difference warrants developing correlation rules and response playbooks rather than putting resources only into expanded blocklists.
Mapping TTPs to the MITRE ATT&CK Matrix
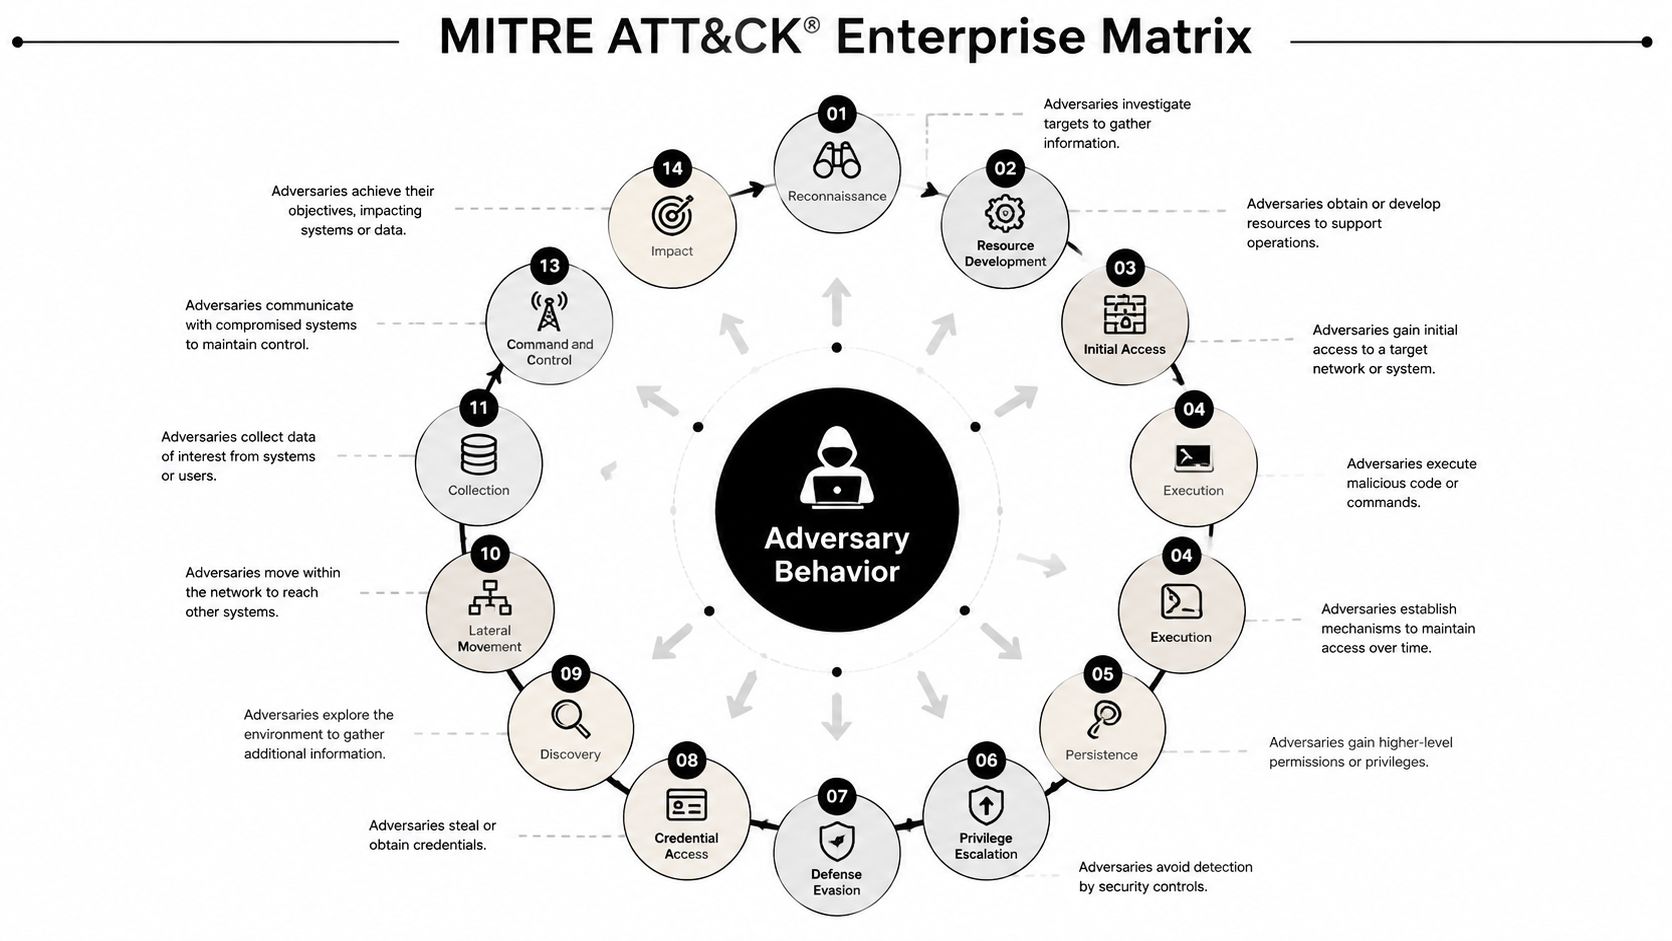
The Enterprise ATT&CK matrix organizes adversary behavior across 14 tactics, covering the attack lifecycle from Reconnaissance and Initial Access through Impact. The live Enterprise matrix enumerates 216 techniques and 475 sub-techniques, according to MITRE ATT&CK. The matrix is not a checklist for every organization to implement uniformly. It is a catalog that helps defenders determine which behaviors their telemetry can see and which stay invisible.
The catalog continues to evolve as adversaries and defenders generate new evidence. According to a 2025 Google Cloud M-Trends report, Mandiant added 2 new techniques, 29 new sub-techniques, and 570 additional mapped techniques in 2024. The same report offers a useful reality check on how prevalent techniques are: Command and Scripting Interpreter appeared in 44.6% of observed cases, Obfuscated Files or Information in 37.3%, and Remote Services in 35.3%. Those numbers are cited in M-Trends 2025.
Technique mappings need implementation context
Security teams commonly map a SIEM detection to the technique level, since that offers a stable category for coverage reporting. The procedure is what makes the rule useful. It captures the command, process relationship, account behavior, cloud action, or system change an actor used.
For instance, a general Command and Scripting Interpreter mapping is not sufficient to create a dependable alert. The rule must know which interpreter appeared, what started it, who executed it, which host was involved, what the command accessed, and whether related events point to execution, discovery, credential access, or lateral movement.
This distinction also guards against a common reporting error. A matrix showing a technique as covered does not prove that the SOC can detect every procedure tied to it. Coverage depends on data quality, collection scope, parser behavior, retention, and the conditions built into the rule.
A practical mapping process should answer:
- Which data source reveals the behavior?
- Which fields pinpoint the procedure instead of only the technique?
- What routine administrative activity looks similar?
- What related events raise confidence?
- What step follows a confirmed match?
Teams can use an ATT&CK framework integration to organize those mappings, yet the framework does not eliminate the engineering effort. It provides that effort with a consistent vocabulary.
Under-Covered TTP Areas Worth Defending
Many TTP explainers continue to focus on phishing attachments, malicious macros, and endpoint malware. Those examples are still relevant, but they no longer capture the full attack surface of a hybrid environment. Three gaps merit immediate attention: identity and cloud abuse, telemetry breadth, and pre-execution reconnaissance.
Identity and cloud activity
Red Canary reported that identity attacks were 4x higher year over year, and that three of its top five observed MITRE ATT&CK techniques were cloud-native and identity-enabled, with Cloud Accounts ranked first. The finding is presented in the 2025 Threat Detection Report.
This alters the evidence defenders require. A cloud account accessed from an unusual context, a newly assigned privilege, an atypical consent action, or a sudden burst of access to sensitive resources may offer more signal than a malware scan on a workstation. Identity logs, cloud audit trails, conditional-access decisions, and SaaS activity thus belong in the same investigation as endpoint process events.
Telemetry breadth
Government guidance cited in MITRE's TTP-Based Hunting paper notes that process monitoring covers 155 techniques, compared with 89 for file monitoring and 85 for command-line parameters. The point is not that process logs solve detection. They do not. The point is that the choice of telemetry directly influences how much of the ATT&CK model a SOC can observe.
File monitoring can reveal what changed. Command-line parameters can expose intent. Process monitoring contributes ancestry, execution context, and relationships among programs. A detection program that gathers only one of these views will generate a coverage chart that appears more complete than the underlying evidence supports.
Reconnaissance before intrusion
Before deploying malware or logging in to a secured system, attackers can gather substantial intelligence. Automated scans, exposed services, discovery of cloud assets, and repeated probes can expose where an organization is vulnerable. In its 2025 update, MITRE expressly added Reconnaissance to ATT&CK Evaluations for cloud security, and Fortinet reported an unprecedented increase in automated scanning as attackers shifted earlier in the intrusion process. This shift is covered in MITRE's cloud security evaluation announcement.
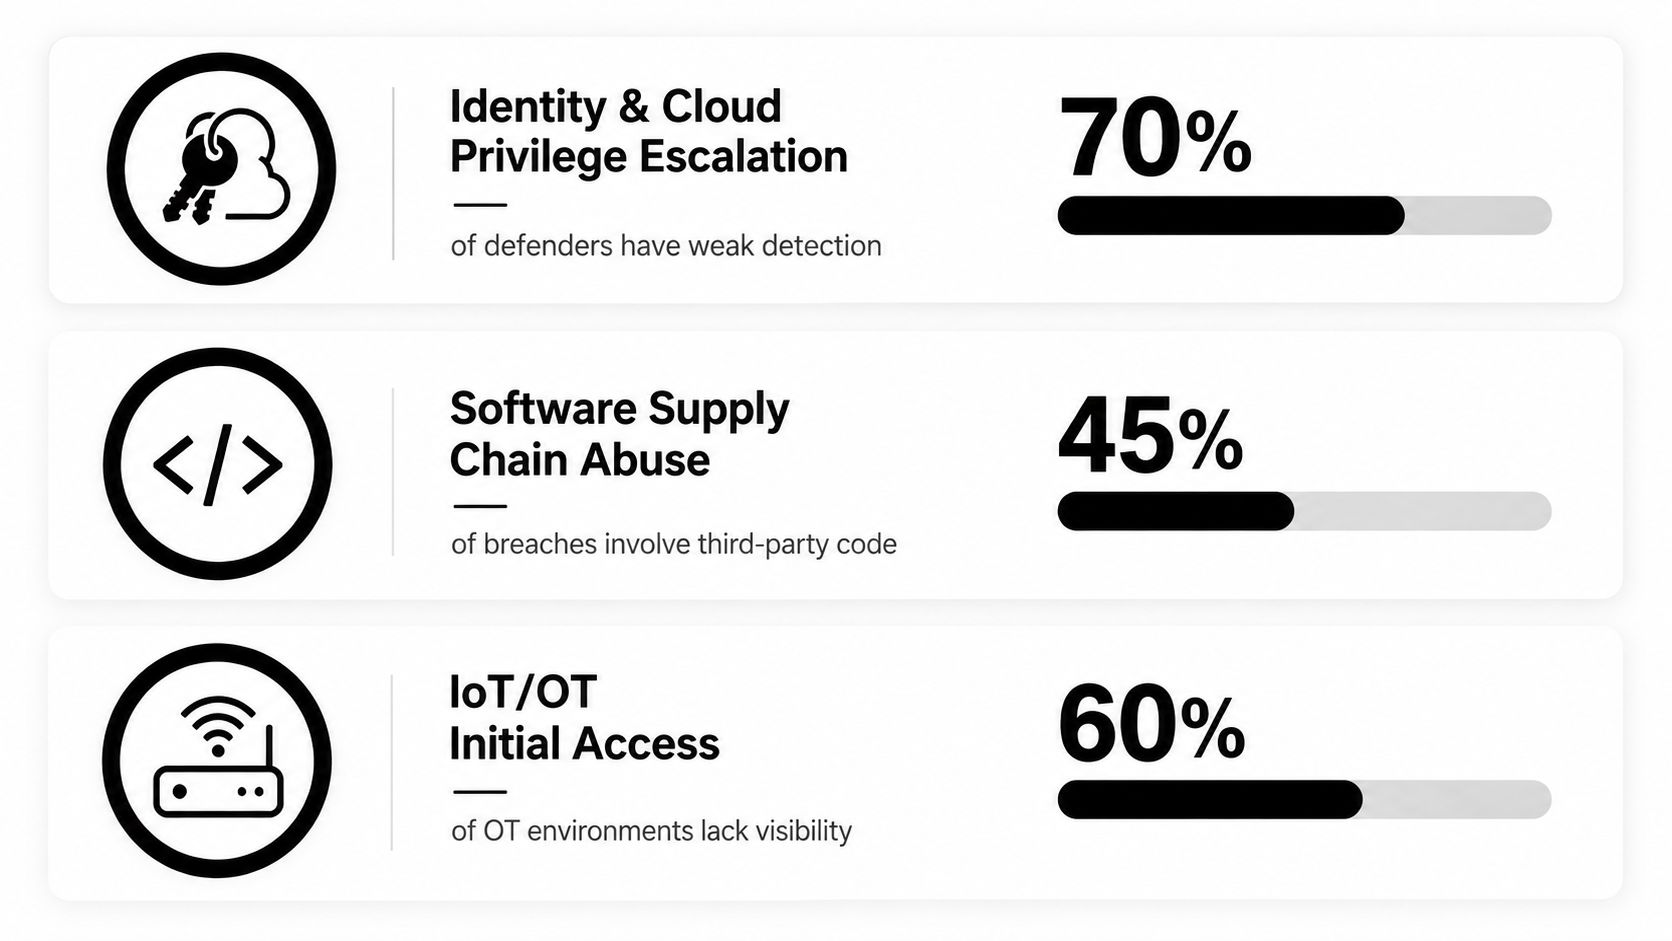
Rather than assigning these areas to separate owners, a modern program should connect them. Cloud access can be clarified by identity signals. Endpoint execution can be confirmed by process telemetry. Reconnaissance data can reveal why a newly exposed asset draws the focus of a later intrusion.
Hypothesis-Driven Hunting and SIEM Correlation Rules
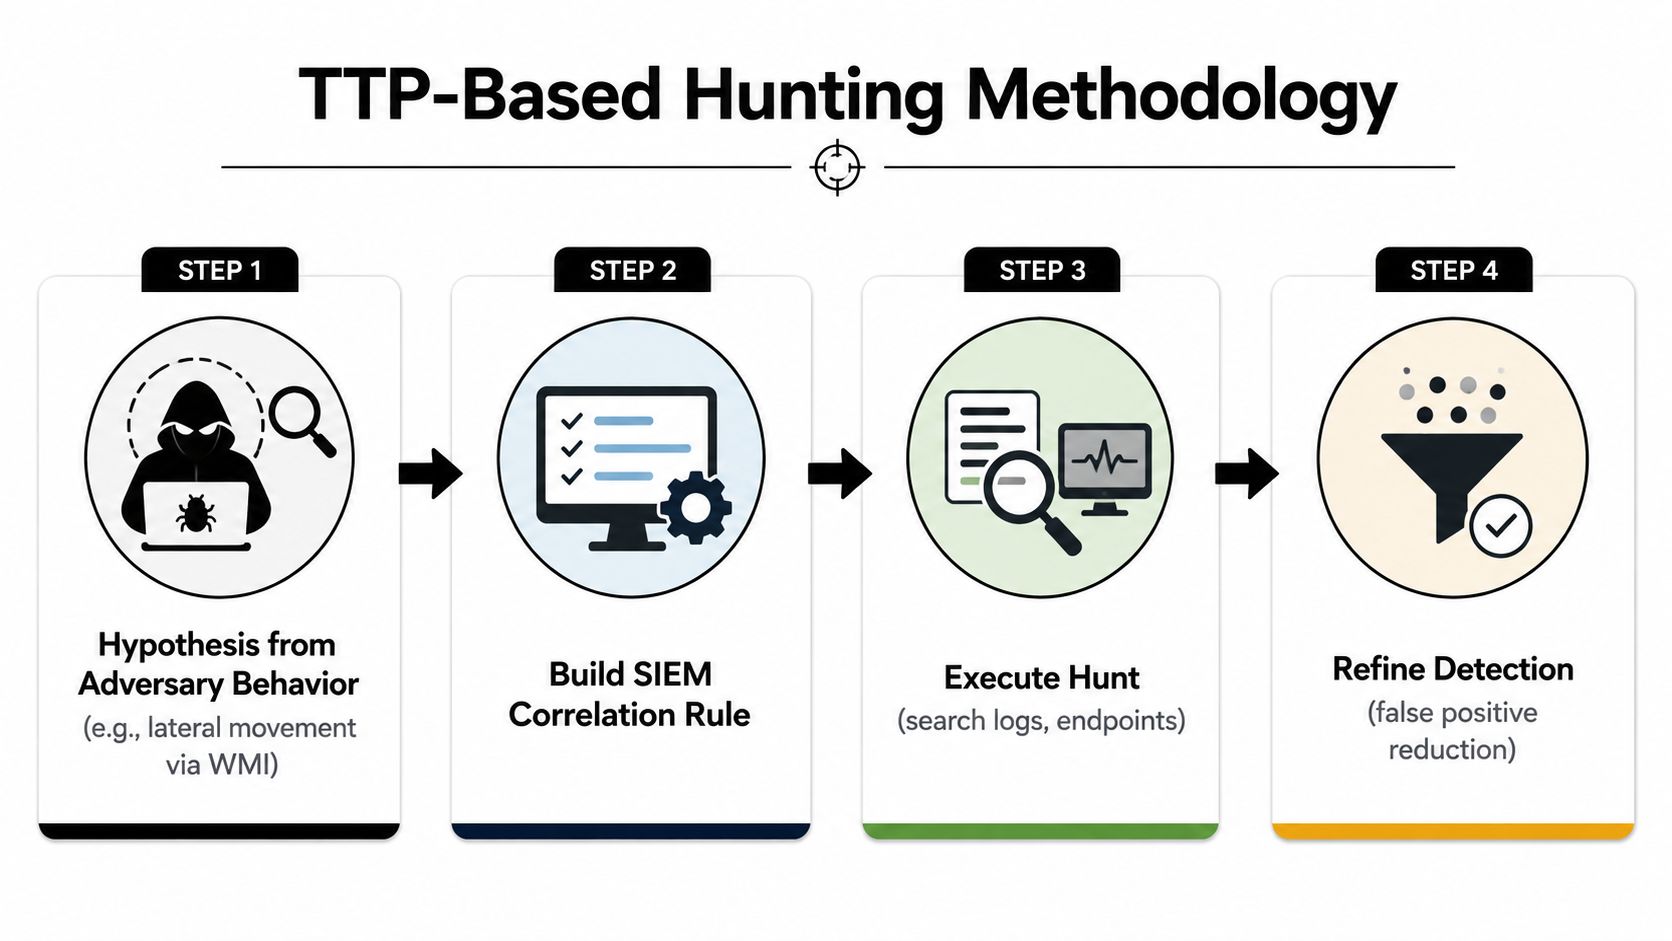
A TTP-based hunt starts by asking which adversary behavior generated the signal, then works backward to define evidence that can be tested. MITRE's TTP-Based Hunting methodology It utilizes hypotheses, abstract analytics, recurring pivots across multiple data sources, and a hunting analysis environment designed for the U.S. Cyber Command's Cyber National Mission Force.
A strong hypothesis remains testable and specific while withstanding shifts in attacker infrastructure. For instance, an adversary may use WMI to move laterally and then spawn a process on a remote host under an atypical account context. The hunt should correlate process creation, authentication, endpoint, and network telemetry rather than match one executable name.
Build the rule around behavior
A SIEM correlation rule ought to join events that represent a sequence or relationship. A lone indicator can trigger enrichment, yet behavior detection requires context. A rule may call for a remote logon, a WMI-related process, an atypical source host, and a destination system the account seldom reaches. Correlation rules that link events together are covered in our SIEM correlation rules guide.
Use a repeatable workflow:
- Form the hypothesis: Specify the adversary action and the observable evidence it leaves.
- Identify data sources: Confirm that endpoint, identity, network, or cloud logs include the necessary fields.
- Write the correlation: Correlate events under suitable time, entity, and context conditions.
- Test historical data: Determine if the logic detects known activity and how much benign activity it captures.
- Run alert-only first: Monitor the rule before allowing automated containment.
- Tune with evidence: Modify exclusions, thresholds, and joins according to analyst outcomes.
Guidance from Hadess on SIEM operations highlights precise logic, historical testing, alert-only rollout ahead of automated response, and false-positive monitoring per rule. It identifies 70% false positives as a threshold that demands immediate attention via tuning, exclusions, or replacement with improved logic.
Threat intelligence can help determine if an identity, domain, or actor profile suits the hypothesis. Teams might review material on open-source intelligence for verifying profiles for enrichment, while anchoring the detection in security telemetry that has been observed.
A durable detection links its rule, triage workflow, response action, and audit trail. Unified Security Stack can hold that context together across SIEM, SOAR, and XDR workflows, enabling analysts to tune correlation logic before response automation takes effect.
Operationalizing TTPs in a Unified SIEM, SOAR, and XDR
A TTP mapping offers little value when it remains just a spreadsheet row. A valuable implementation links collection, normalization, correlation, triage, response, and evidence. Unified Security Stack offers an example of a unified SIEM, SOAR, and XDR approach to that workflow.
The platform collects telemetry from cloud services, network devices, and endpoints via APIs, Syslog, NetFlow, and agents. It correlates events in real time before indexing to cut noise, which is important when a detection relies on relationships among events instead of a single log line.
Start with the evidence needed for the technique
The modular stack covers log management, vulnerability scanning, access rights auditing, endpoint protection, dark web monitoring, and file tracking. These sources handle distinct parts of the TTP problem:
- Endpoint and process telemetry reveals execution and persistence behavior.
- Access-rights information helps detect privilege and identity misuse.
- Vulnerability and asset data provides context about exposure.
- Network and flow telemetry enables analysis of lateral movement and command-and-control.
- File tracking helps detect changes tied to defense evasion or persistence.
The goal isn't to gather everything without discrimination. It's to gather the fields needed to test the procedures behind the techniques. A matrix entry labeled covered should link to a real event source, a parser, a rule, an analyst workflow, and a response decision.
Connect detection to triage and containment
Imagine a correlation rule detects a suspicious cloud account action that is followed by endpoint access and a remote administrative connection. The rule associates the activity with appropriate ATT&CK techniques and generates an alert containing the related entities. An embedded large language model can support alert triage, produce a summary of the event chain, and help analysts adjust the rule to cut down false positives. Human oversight remains essential, especially before any response action impacts a privileged account or production host.
The SOAR layer can subsequently execute a standard or custom playbook. Based on the organization's approval model, this might include endpoint isolation, account disablement, extra evidence collection, or incident channel notification. The key design decision is to preserve traceability: the behavior that triggered the playbook, the analyst's reasoning, the response action, and the outcome should stay linked.
Organizations evaluating threat detection and response solutions should review the whole chain, not merely how many integrations exist. A platform may collect data from numerous sources yet still fall short if analysts have to switch among separate consoles to interpret an alert or demonstrate what occurred.
Preserve compliance evidence as a byproduct
Unified workflows can map detections and collected evidence to CMMC, HIPAA, SOC 2, ISO 27001, PCI, GDPR, and GLBA. Compliance value stems from maintaining the operational record, not from adding a framework label after an incident. When logs, rule logic, alert decisions, response actions, and review history stay linked, they create a stronger and more defensible evidence trail.
Unified Security Stack also provides a threat library with more than 30 billion IOC elements. Those elements can add reputation and context to a TTP-driven investigation, yet they should not take the place of behavioral detections. The most effective design uses the library to increase confidence while the correlation rule clarifies what the actor did.
Tuning, Triage, and Compliance Evidence on One Loop
The operational benefit of TTP-driven defense becomes evident after the initial alert. Analysts adjust the detection, hunters validate the hypothesis with new data, responders refine the playbook, and compliance teams repurpose the same records as evidence. That feedback cycle offers greater value than a static ATT&CK coverage report, since every function strengthens the others.
A single investigation can produce several useful outputs:
- Detection evidence: The source events and normalized fields that back the technique mapping.
- Tuning evidence: The exclusion, threshold, or condition that was modified following analyst review.
- Response evidence: The playbook action, approval, execution outcome, and recovery measure.
- Audit evidence: The timestamps, ownership, review history, and control mapping needed for HIPAA, GLBA, CMMC, PCI, or ISO 27001 efforts.
The discipline itself is straightforward, yet it requires consistent enforcement. Begin with the ATT&CK techniques most relevant to your environment, link each to the telemetry and rules that detect it, and confirm that the generated alert can yield evidence an auditor can follow.
A practitioner checklist
- Map your top 20 ATT&CK techniques: Tie every technique to defined SIEM rules, data sources, procedures, and accountable owners.
- Control false positives: Use LLM-assisted triage and rule tuning to push noisy detections below the 70% false-positive threshold outlined in the SIEM operations guidance.
- Stage response automation: Before allowing containment or account actions, run new playbooks in alert-only mode.
- Validate the evidence path: Ensure each mapped technique generates the logs, alert history, response record, and control mapping that an auditor might request.
- Review coverage by environment: Evaluate identity, cloud, endpoint, network, and reconnaissance visibility independently instead of depending on a single aggregate score.
A unified, open-source SIEM, SOAR, and XDR platform can hold this loop within a single operating model. For mid-sized and enterprise teams, that lowers the friction of managing separate consoles for detection, response, threat intelligence, and compliance reporting. Unified Security Stack is supported by Linux Foundation membership and extensive integrations, and its open-source licensing model eliminates per-event costs while enabling a consolidated workflow.
Unified Security Stack brings together SIEM detection, SOAR playbooks, XDR telemetry, ATT&CK-aligned correlation, LLM-assisted triage, and compliance evidence management within one platform. Visit Unified Security Stack to see how its unified workflow can help your team transform TTPs into adjustable detections, controlled response actions, and audit-ready records.