SIEM as a Service
SIEM-as-a-Service (SaaS) and Managed SIEM services have become popular with companies seeking to satisfy security compliance standards affordably. Let's examine why a SIEM service can change the cybersecurity of your small or mid-sized business.
What does SIEM-as-a-Service (SaaS) mean?
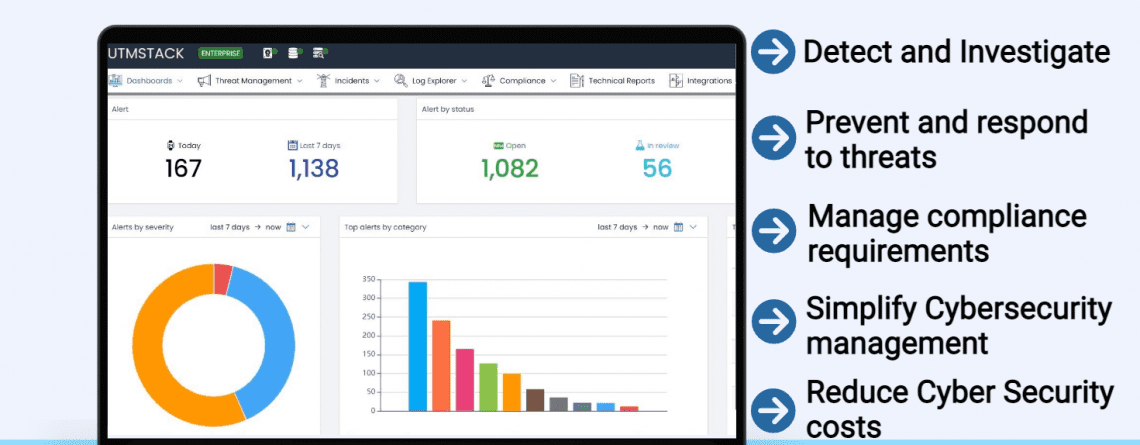
Security Information and Event Management (SIEM) is software that connects with various applications and gathers information from every data source as event logs. Such data are correlated and assessed in an event correlation engine to identify any intrusion attempt through behavior patterns. Then, SIEM issues alerts and displays events on one interface when deviations from normal behavior happen. This lets the SIEM service provider monitor and analyze your infrastructure logs to respond to incidents immediately.
Why should your organization implement a SIEM service?
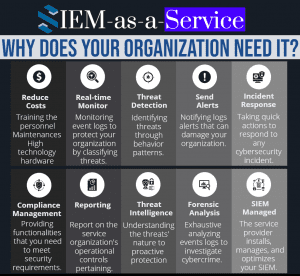
Managing a SIEM is a complex process that not all organizations can take on. Some prefer to contract a SIEM service because of the time, effort, and money that should be invested to train personnel operating with SIEM. In essence, these services include a high-quality expert team to monitor your event logs in real time, detect cyber security threats, manage compliance, respond to incidents, and even perform forensic analysis.
On the other hand, it's no secret that this innovative technology is usually costly for small and mid-size businesses. Although SMBs can find excellent cost-effective SIEM such as Unified Security Stack, it would not be wrong to acquire a service with stronger financial advantages for your budget.
An on-premise SIEM overseen by the organization's security team needs extra payments for maintenance and advanced technology hardware to manage sophisticated threats. Thus, this circumstance renders the product expensive. As a remedy, SIEM vendors deliver a cost-effective on-premise and cloud SIEM managed service. Serving as an extension of your current security team, installing, managing, and optimizing SIEM software.
In general, if you deploy a SIEM-as-a-Service (SaaS), you will get the following benefits:
- Reduce costs: Companies do not have to pay for personnel training, maintenance, or high technology hardware.
- Real-time Monitor: Observing event logs to safeguard your organization through threat classification.
- Threat Detection: Detecting threats using behavior patterns.
- Send Alerts: Sending log alerts that can harm your organization.
- Incident Response: Acting fast to respond to any cybersecurity incident.
- Compliance Management: Delivering the capabilities required to satisfy security requirements.
- Reporting: Report covering the service organization's operational controls as they pertain.
- Threat Intelligence: Grasping the nature of threats and vulnerabilities for proactive protection and reducing the risk from attacks.
- Forensic analysis: Thorough analysis of event logs to investigate cybercrime.
- SIEM Managed: The service provider's expert team ensures your SIEM is installed, managed, and optimized.
Cost-effective Unified Security Stack Service
Unified Security Stack provides affordable SIEM services to safeguard the environment of any organization with hybrid, on-premise, or cloud infrastructure. Because Unified Security Stack uses a Next-Gen SIEM technology, experienced security experts, and updated threat intelligence, you can improve risk management throughout your environment.
If you would like to learn more about how Unified Security Stack can make your cybersecurity management and compliance simpler, request a free demo of our services today.
We would be glad to show you how we can protect your digital assets and IT infrastructure.