Cost-effective Managed SIEM Service
Contracting with a third party for managed SIEM services is increasingly affordable and requested by organizations of all sizes. Undoubtedly, the benefits linked to this service enable monitoring, analyzing, and responding to cyber security threats more cost-effectively. However, what exactly is a managed SIEM? Is price the only feature to consider? What distinguishes a managed SIEM Provider (MSP) from a Managed Security Service Provider (MSSP)?
What is a Managed SIEM?
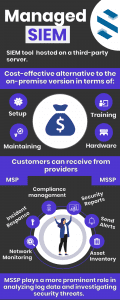
A managed Security Information and Event Management (SIEM) is a cost-effective substitute for the on-premise version. This happens because the application is hosted on the server of a third-party service provider. Consequently, organizations pick this option to reduce setup, maintenance, hardware, and training costs, using the knowledge of cyber security specialists who analyze data stored in SIEM to identify Indicators of Compromise (IoC).
In addition, a managed SIEM is a highly rated service for reducing the risk of security breaches in organizations. This is achievable through MSPs that are extensively trained in network monitoring, incident response, and compliance management, securing your business without any work on your part.
Managed SIEM Provider (MSP) and Managed Security Service Provider (MSSP)
Frequently, organizations are unsure how to decide if hiring an MSP or an MSSP is better. Both an MSSP and an MSP provide monthly security reports, monitor network security events, and alert their customer when any anomaly is detected. Still, a Managed Security Service Provider takes on a greater role in examining log data and investigating security threats.
The MSP is able to apply patches and updates, oversee compliance, maintain the SIEM setup, and carry out asset inventory tasks. An MSSP hosts, deploys, and manages a security infrastructure while delivering information security services to numerous organizations at the same time.
Due to an MSSP managing SIEM tools, Intrusion Detection Systems/Intrusion Prevention Systems, firewalls, anti-virus, vulnerability, compliance management, and more, it turns into a full package for safeguarding organizations.
Today, most SIEM tools providers like Unified Security Stack include in their business portfolios partnerships strategic with well-reputed MSP and MSSP. This lets customers obtain powerful tools, resources, expertise, and the latest tech innovations to detect advanced threats.
Unified Security Stack Managed SIEM Service
Unified Security Stack is a Next-Gen SIEM provider that delivers a cost-effective managed SIEM service. Inside what it provides, you can discover:
- Log Management.
- Dashboard Builder.
- Vulnerability Management
- Identity Management.
- Incident Response.
- HIDS and NIDS.
- Monitoring of cloud platforms (AWS, Azure).
- Compatibility with Endpoint Protection.
- Compliance Management.
- Custom reports.
- Tracking and classification of files.
- Threat Intelligence.
- No restrictions on the number of data sources.
- Unlimited scaling.
- Retention of logs for 15 months.
- Enterprise assistance delivered by phone and email, 24/7/365.
- Unified Security Stack engine updates happen every day.
- Experts at Unified Security Stack handle the installation and hosting on your behalf.
- Monitoring, alerting, incident response, and compliance management around the clock.
- Forensic analysis.
Conclusion
The managed SIEM from Unified Security Stack delivers a cost-effective solution to monitor your organization and improve threat detection and incident response regardless of your IT infrastructure. Whether you want to deploy a hybrid, on-premise, or cloud SIEM, the team of security experts that manages the SIEM should possess adequate expertise. Thus, before taking advantage of an MSP or MSSP offering, you must make sure the services provided align with the requirements of your organization. In this way, you will obtain strong value for money and security coverage that meets the best cybersecurity practices.