Author - SYNOTI

Automated Vulnerability Scan To Protect Your Business

What Is a Vulnerability Scan? A vulnerability scan is an automated procedure for detecting vulnerabilities, or security holes, in software, operating systems, or networks that malicious actors could exploit. Essentially, it is a core part of vulnerability management aimed at shielding organizations from breaches and the leakage of sensitive data. Vulnerability Scan vs. Penetration Testing Vulnerability scanning and penetration testing are sometimes mistaken for one another...
Multi-tenant Cloud Architecture

Over the years, organizations have come to recognize the advantages of deploying a Cloud-based SIEM Service in relation to scalability, cost, and security. Before running in the cloud, though, you need to understand which architecture to adopt to safeguard your business and your customers' data. To help you put a cost-effective SaaS SIEM Service into practice, we share...

Best Dark Web Monitoring Tools

The dark web is a portion of the internet that search engines do not index and that can be reached only via certain browsers. It has turned into a refuge for numerous illegal activities and for individuals seeking anonymity, hackers included. Hackers frequently use the dark web to sell stolen passwords, undermining employee security and...

SIEM as a Service

Organizations that need to satisfy security compliance standards affordably have increasingly turned to SIEM-as-a-Service (SaaS) and Managed SIEM offerings. Here, we examine how a SIEM service can improve cybersecurity for your small or mid-sized business. What does SIEM-as-a-Service (SaaS) mean? Security Information and Event Management (SIEM) is software that connects to multiple applications and gathers information from each data source in the form...

Cost-effective Managed SIEM Service

Contracting with a third party for managed SIEM services is becoming more affordable and is sought after by organizations of all sizes. The benefits tied to this service undoubtedly enable monitoring, analysis, and response to cyber security threats in a more cost-effective way. Yet what exactly is a managed SIEM? Is price the only factor to consider? What distinguishes a managed...

A CMMC Compliance Checklist

The Cybersecurity Maturity Model Certification (CMMC) is a widely recognized framework for evaluating how mature an organization's cybersecurity is. It is intended to assist organizations in strengthening their cybersecurity by increasing awareness of best practices and putting a roadmap into place. On November 4, 2021, the Department of Defense revealed the strategic direction of the Cybersecurity Maturity Model Certification (CMMC) program, which marked the completion of an...

How a Dark Web Monitoring Can Save Your Organization

Companies frequently have their confidential information illegally offered for sale on the darknets without realizing it. According to statistics, more than 75% of compromised credentials are reported to the victim organization by law enforcement only after it is too late. This is why providers of dark web monitoring tools are the right solution to help you learn in time when your credentials have been stolen...

Using event correlation and AI for Threat Detection and Incident Response

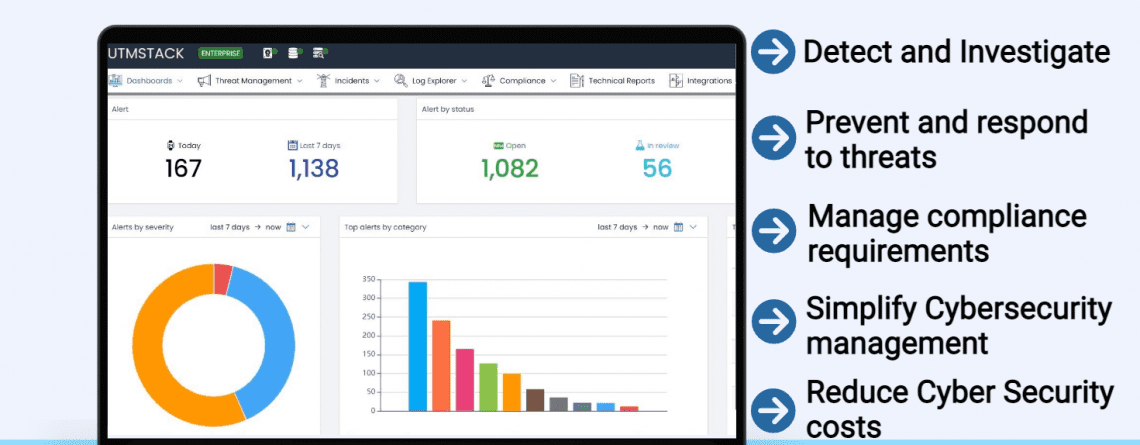
Unified Security Stack is a forward-looking Security Information and Event Management (SIEM) solution that uses real-time correlation and artificial intelligence (AI) for sophisticated threat detection. The following is a thorough review of how Unified Security Stack applies these technologies: Real-Time Event Correlation The event correlation tool inside Unified Security Stack’s SIEM framework collects and examines log data from a broad range of network applications, systems, and devices. This analysis is...

What exactly is a Cloud SIEM? The downsides, the upsides, and the difficulties.

Security Information and Event Management (SIEM) is software that gathers security information from various sources, examines log data, and spots patterns that could signal a threat or breach. With SIEM, IT teams can detect and respond to many threats across networks in real time. Traditional on-premises SIEMs, however, are falling behind and are being replaced by new security focuses...

In what way do AWS Security Groups function?

AWS Security Groups serve as critical components that help shield your resources on Amazon Virtual Private Cloud (Amazon VPC). With Security Groups, you can determine which types of traffic may reach your resources, for example, specific ports, source IP ranges, or even protocols. Next, you will soon discover how AWS Security Groups function with their default inbound and outbound rules. What exactly are AWS Security Groups? AWS Security...

Skip to content