What Is Threat Intelligence: Guide to Proactive Security
Threat intelligence is evidence-based knowledge about current or new cyber threats, assembled from context, mechanisms, indicators, implications, and action-oriented guidance rather than raw data alone. Operationally, this structured approach converts dispersed logs, malware artifacts, adversary behavior, and outside reporting into choices your security team can make before the next alert becomes an incident.
If security teams are asking what threat intelligence is, they are already experiencing the problem. The SIEM is taking in logs. EDR is generating detections. The XDR console is crowded with events. Compliance teams still require evidence for HIPAA, PCI, GLBA, CMMC, or ISO 27001, and the SOC keeps repeating one question: which alerts actually matter?
Threat intelligence proves its value in that space between data and decision. A mature program does not merely gather indicators. It shows analysts which adversary behaviors matter, which exposures connect to business risk, which detections need tuning, and which events ought to initiate automated response. Within an integrated SIEM, SOAR, and XDR stack, threat intelligence turns operational. It powers correlation rules, provides enrichment for investigations, backs response playbooks, and gives compliance reporting sufficient context to withstand an audit.
Table of Contents
- From Reactive Alerts to Proactive Defense
- The Four Levels of Threat Intelligence
- The Six-Stage Threat Intelligence Lifecycle
- Activating Intelligence in Your SIEM SOAR and XDR
- Measuring the ROI of a Threat Intelligence Program
- How to Build Your Threat Intelligence Program
- Conclusion Intelligence Is Your Proactive Edge
From Reactive Alerts to Proactive Defense
A reactive SOC often appears active yet lacks visibility. Analysts handle alerts one by one, search for absent context across disconnected tools, and escalate incidents according to severity labels that frequently reveal more about the product than the business impact.
That approach fails quickly in modern environments. Cloud logs, endpoint telemetry, identity events, firewall records, and vulnerability findings each arrive at varying speeds and in varying formats. Without context, the team uses time wondering whether an alert has meaning rather than determining the next step.
According to a 2023 Gartner-based definition summarized by CrowdStrike, threat intelligence is “evidence-based knowledge (e.g., context, mechanisms, indicators, implications, and action-oriented advice) about existing or emerging menaces or hazards to assets.” This distinction matters because it separates intelligence from raw feed data. A simple list of suspicious file hashes is insufficient. A useful intelligence product describes what the indicator concerns, how the attack operates, why it matters in your environment, and which controls need adjustment.
What changes when context is present
When threat intelligence functions well, the SOC no longer handles each alert as a standalone event.
Instead, teams can answer questions like these faster:
- Relevance to assets: Is this behavior aimed at workloads, identities, or data stores we run?
- Attacker behavior: Does this connect to a recognized tactic, technique, or procedure that ought to shape correlation logic?
- Priority: Should exploitability, exposure, or business impact take priority in the incident queue?
- Action: Should we enrich, contain, block, isolate, escalate, or simply document?
Practical rule: If intelligence fails to alter a detection, a triage decision, a response playbook, or a reporting outcome, it remains only data.
Here, too, threat intelligence meets vulnerability management. Security teams often struggle because patch backlogs and exposure lists exceed the time available. A helpful companion discipline is prioritizing security fixes with risk scores, which helps turn broad technical findings into remediation prioritized by business needs.
Real-time correlation is critical when teams want to connect intelligence straight into operations. A unified platform for real-time threat detection provides threat indicators, event patterns, and analyst rules a place to converge in production rather than remain separate spreadsheets and browser tabs.
What doesn't work
Several patterns fail repeatedly in the field:
- Feed hoarding: A greater number of feeds does not automatically enhance detection quality.
- No business scoping: Intelligence teams that fail to align with crown-jewel assets create interesting reports, not useful results.
- Manual-only enrichment: Analysts cannot continue copying hashes, URLs, and actor notes into each case by hand.
- Compliance isolation: If TI never contributes to audit evidence, regulated teams forfeit a major portion of its value.
Threat intelligence is a practice of operational rigor. Executed properly, it provides analysts with usable signal, detection engineers with improved logic, and compliance teams with contextual evidence.
The Four Levels of Threat Intelligence
Threat intelligence is not a single item. It consists of layers, and every layer supports a distinct decision-maker. When those layers are blended, executives receive raw indicators they cannot apply, and analysts receive broad strategic overviews that do not assist with incident closure.
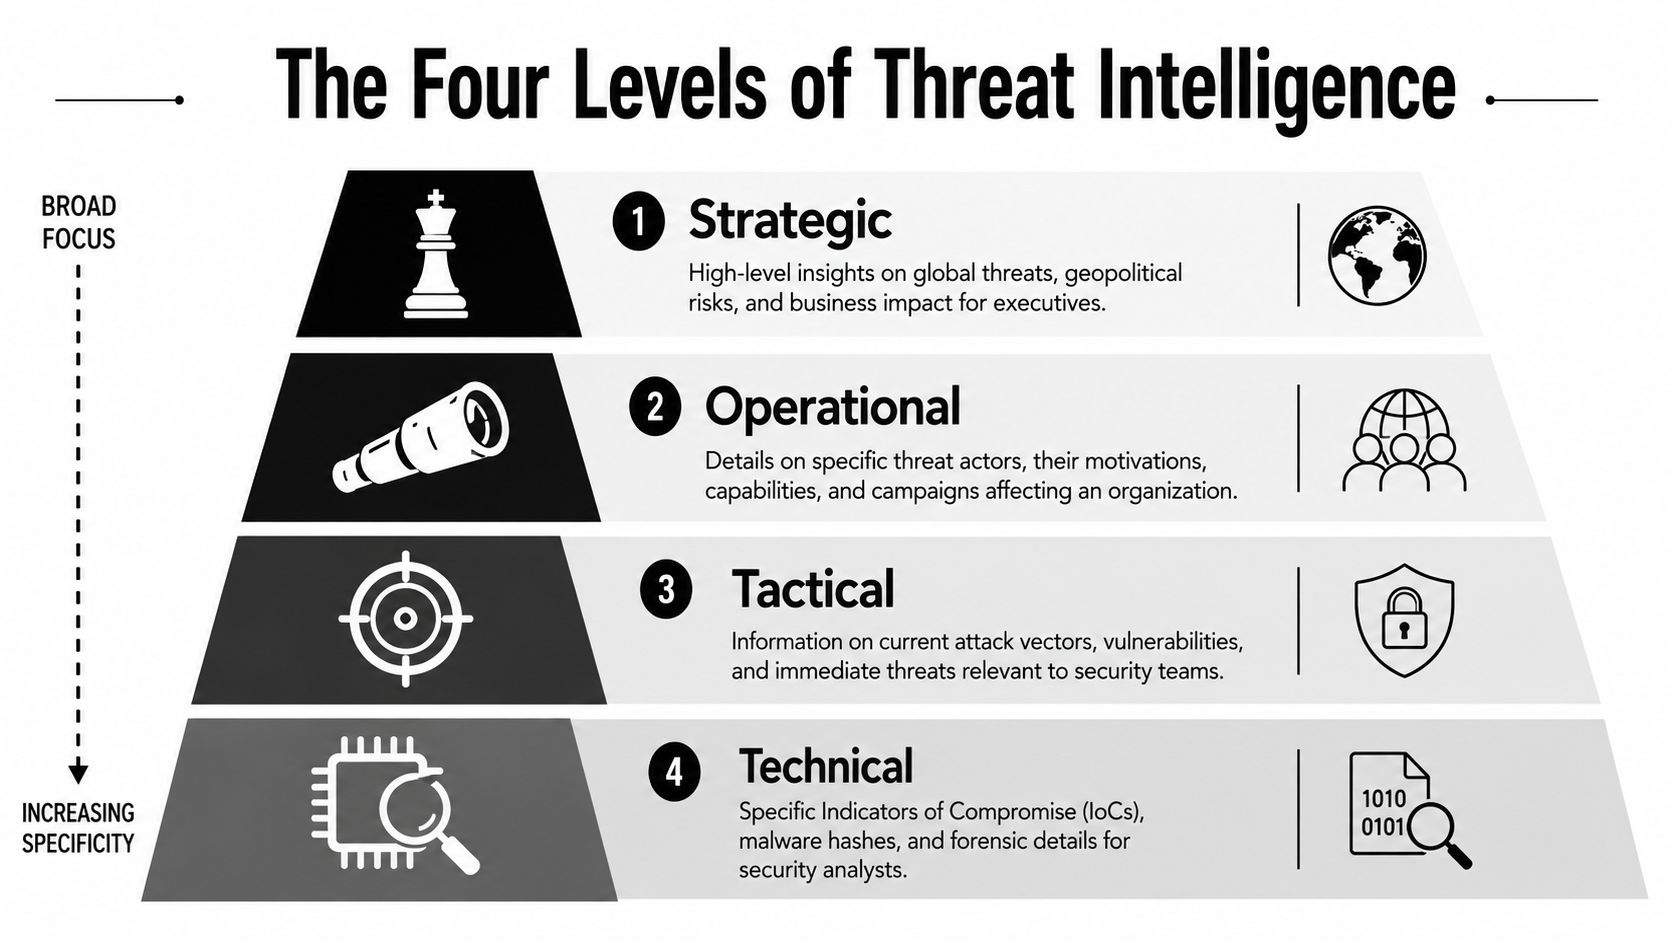
One useful way to view the stack is this: as you move upward, the audience becomes wider and the decision timeframe extends further. As you move downward, the data becomes more detailed and its operational application becomes more urgent.
| Intelligence Type | Audience | Purpose | Example |
|---|---|---|---|
| Strategic | CISO, board, risk leaders | Guide security investment and business risk decisions | Assessment of threats most relevant to a regulated healthcare provider |
| Operational | Incident response, threat hunting leads | Understand campaigns, actor motives, and likely next steps | Analysis of a phishing campaign targeting finance staff |
| Tactical | Detection engineers, SOC leads | Improve defensive controls around attacker behavior | Mapping detections to attacker TTPs for credential abuse |
| Technical | SOC analysts, SIEM engineers | Trigger detections and enrich investigations | Malicious file hashes, URLs, or other observed artifacts |
Strategic intelligence
Strategic intelligence is produced for executives who set budget, policy, staffing, and risk posture. It ought to clarify which threat trends are relevant to the organization's sector, where exposure is growing, and which control gaps warrant funding.
This tier is not concerned with placing malware samples into a board presentation. It is concerned with supporting decisions. Within a PCI or HIPAA setting, strategic intelligence can guide where logging depth, endpoint coverage, identity controls, and third-party monitoring must be enhanced.
Operational intelligence
Operational intelligence is positioned nearer to live adversary operations. Its focus includes campaigns, the motivations of threat actors, targeting trends, and how attacks advance.
Incident responders rely on this layer when they must understand what an intrusion may evolve into, rather than only what has already occurred. Threat hunters also use it to build hypotheses about persistence, credential access, lateral movement, or data staging. Teams engaged in threat hunting techniques in 2026 need this layer because it helps convert broad suspicion into specific hunting paths.
Operational intelligence is the point at which a set of related events begins to resemble a campaign rather than an arbitrary group of alerts.
Tactical intelligence
Tactical intelligence enables defenders to grasp how attackers function. It frequently focuses on TTPs, adversary tradecraft, and defensive ramifications.
This is the layer detection engineers rely on to address questions such as: Should this PowerShell behavior generate an alert? Which authentication anomalies fit within a correlation rule? What endpoint telemetry should be kept because it supports a particular technique?
Tactical intelligence lasts long enough to inform detections, yet remains precise enough to affect engineering decisions.
Technical intelligence
The technical layer is the most concrete. It includes indicators and forensic artifacts that systems can consume directly. Microsoft points out that for SIEM solutions like Microsoft Sentinel, the most frequent form of CTI is threat indicators, also known as IOCs or indicators of attack, which associate observed artifacts such as URLs, file hashes, or IP addresses with known threat activity in its Sentinel threat intelligence overview.
Numerous programs begin with this method, and that is acceptable. Yet technical intelligence by itself has boundaries. Indicators age out, infrastructure changes, and static matches overlook behavior that a TTP-based rule would detect.
A mature program requires all four levels. Strategic defines priorities. Operational contextualizes the threat. Tactical adjusts defenses. Technical fuels machines.
The Six-Stage Threat Intelligence Lifecycle
Threat intelligence does not become fully formed simply because someone subscribed to a feed. It emerges from a repeatable process that converts raw collection into outputs usable by analysts and leaders.
Why the lifecycle matters
This field was not always so structured. The FIRST CTI curriculum introduction notes that the formalization of threat intelligence definitions in 2014 by groups including the Bank of England Cyber Working Group represented a major milestone, defining it as a separate professional discipline with a structured process rather than an improvised analytical activity.
That history is important because many organizations continue to handle TI as improvised collection. Someone stores links, moves indicators into a spreadsheet, and sends sporadic emails to the SOC. That is not a program. It does not scale, and it does not generate consistent outputs for SIEM rules, XDR enrichment, or audit evidence.
The six stages in practice
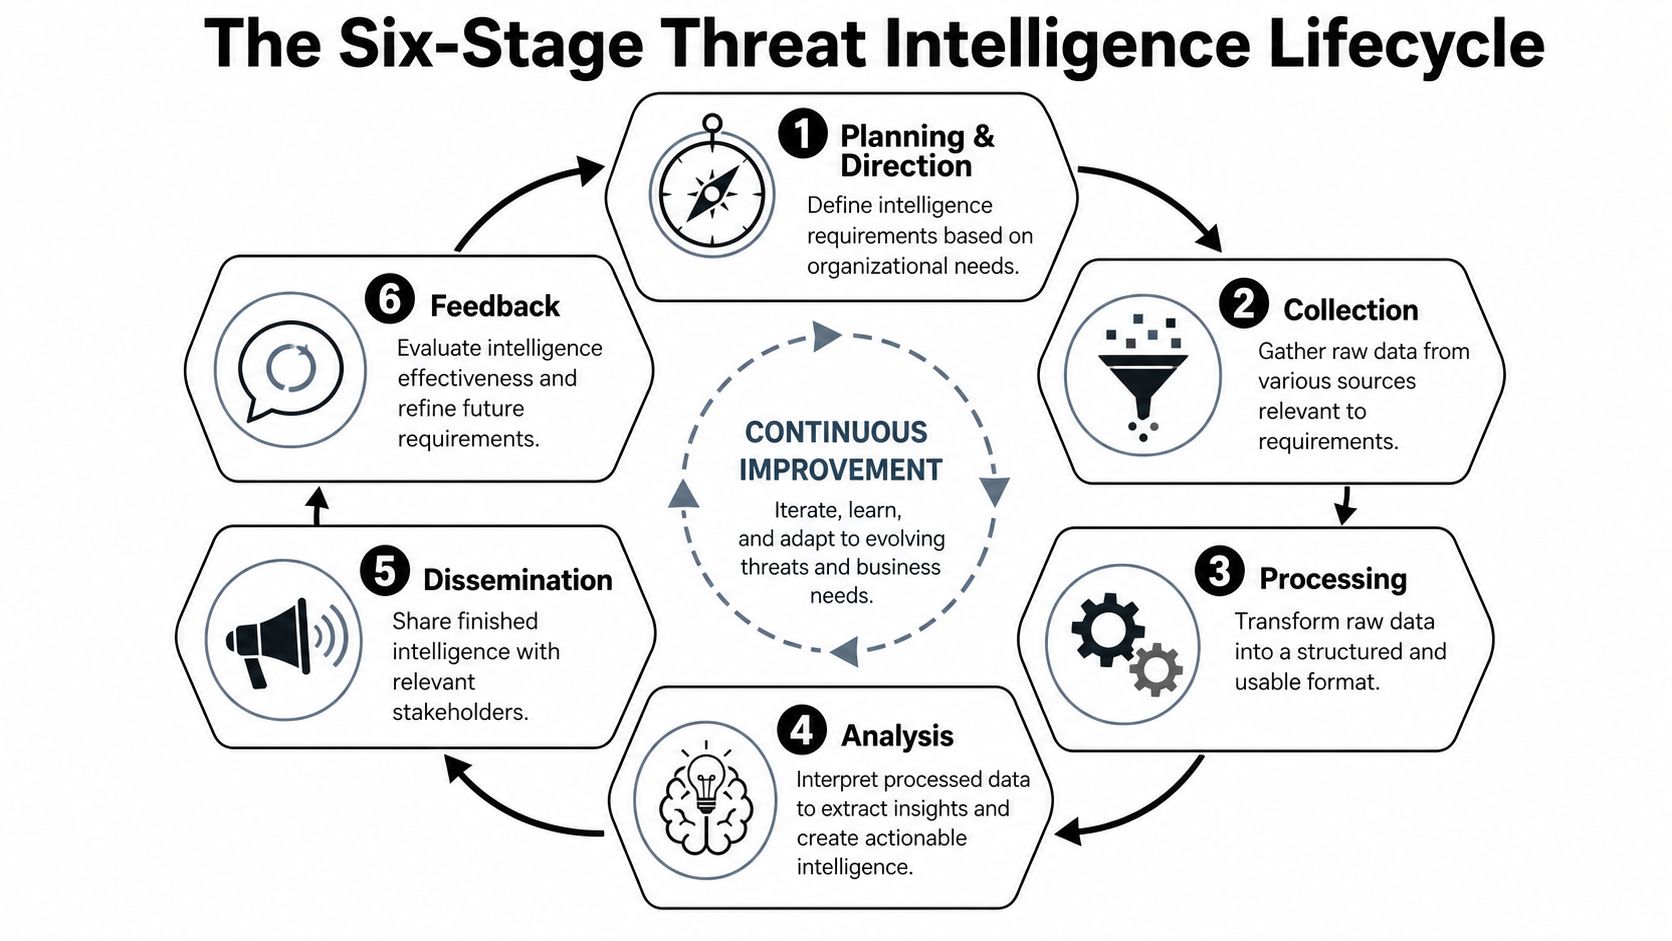
The traditional lifecycle consists of six phases. Every phase serves an operational purpose.
Planning and direction
Begin with intelligence requirements. Which business services are most important? Which regulatory obligations generate logging and evidence needs? Which attack paths concern you most at present? Effective planning avoids the frequent error of gathering everything and applying almost none of it.Collection
Collect raw material from internal and external sources. Internal sources cover endpoint logs, authentication events, case data, and alerts that could point to a breach. External sources may encompass OSINT, vendor reporting, malware analysis, and monitoring of actor tactics. Collection must be driven by requirements, not curiosity.Processing
Raw data must be made usable. Standardize fields, remove duplicate records, parse observables, and map artifacts into a format that SIEM, SOAR, or TIP can ingest. If your engineering team omits this step, analysts are left with the mess.
Nothing erodes confidence in a threat intelligence program faster than sending unvetted observables straight into production detections.
Analysis
Here is where intelligence actually becomes intelligence. Analysts link attacker behavior, infrastructure, timing, victimology, and business relevance. Valuable outputs clarify not only what was observed, but why it matters and what actions should come next.Dissemination
Send the completed product to the appropriate audience in the appropriate format. Executives require risk framing. SOC teams require enriched alerts, watchlists, and updated detections. Compliance teams require reporting that connects observed threats and responses to control objectives.Feedback
Complete the feedback loop. Ask if the intelligence altered a detection, enhanced triage, or supported an audit. If it did not, the next cycle should revise requirements, source quality, or dissemination approach.
An effective lifecycle operates less like a research library and more like a production system. Inputs are chosen purposefully, transformed with care, and delivered in formats operations teams can use without additional translation.
Activating Intelligence in Your SIEM SOAR and XDR
Threat intelligence begins to deliver value when it no longer stays in reports and starts influencing live detections. In an integrated security stack, intelligence serves as input for correlation rules, enrichment for investigations, and a trigger for automated action.
Where intelligence enters detection engineering
Gartner's definition is directly relevant here because SIEM systems use threat intelligence to create rules around attacker tactics, techniques, and procedures alongside known indicators of compromise, as summarized in Exabeam's explanation of threat intelligence in SIEM.
That shows up in operations in two main ways:
- Indicator-driven detections use specific observables, including suspicious URLs, file hashes, or other artifacts, that can be matched against incoming telemetry.
- Behavior-driven detections use intelligence about attacker tradecraft to create rules for sequences, anomalies, and control bypass attempts.
The first model is simple and quick to deploy. The second model is more difficult to engineer but typically more resilient when adversaries change infrastructure.
A mature SOC employs both. If your SIEM matches only static indicators, it will overlook attacks that reuse methods but not the same infrastructure. If it models only behavior, you may overlook simple high-confidence hits that a curated IOC set would have caught right away.
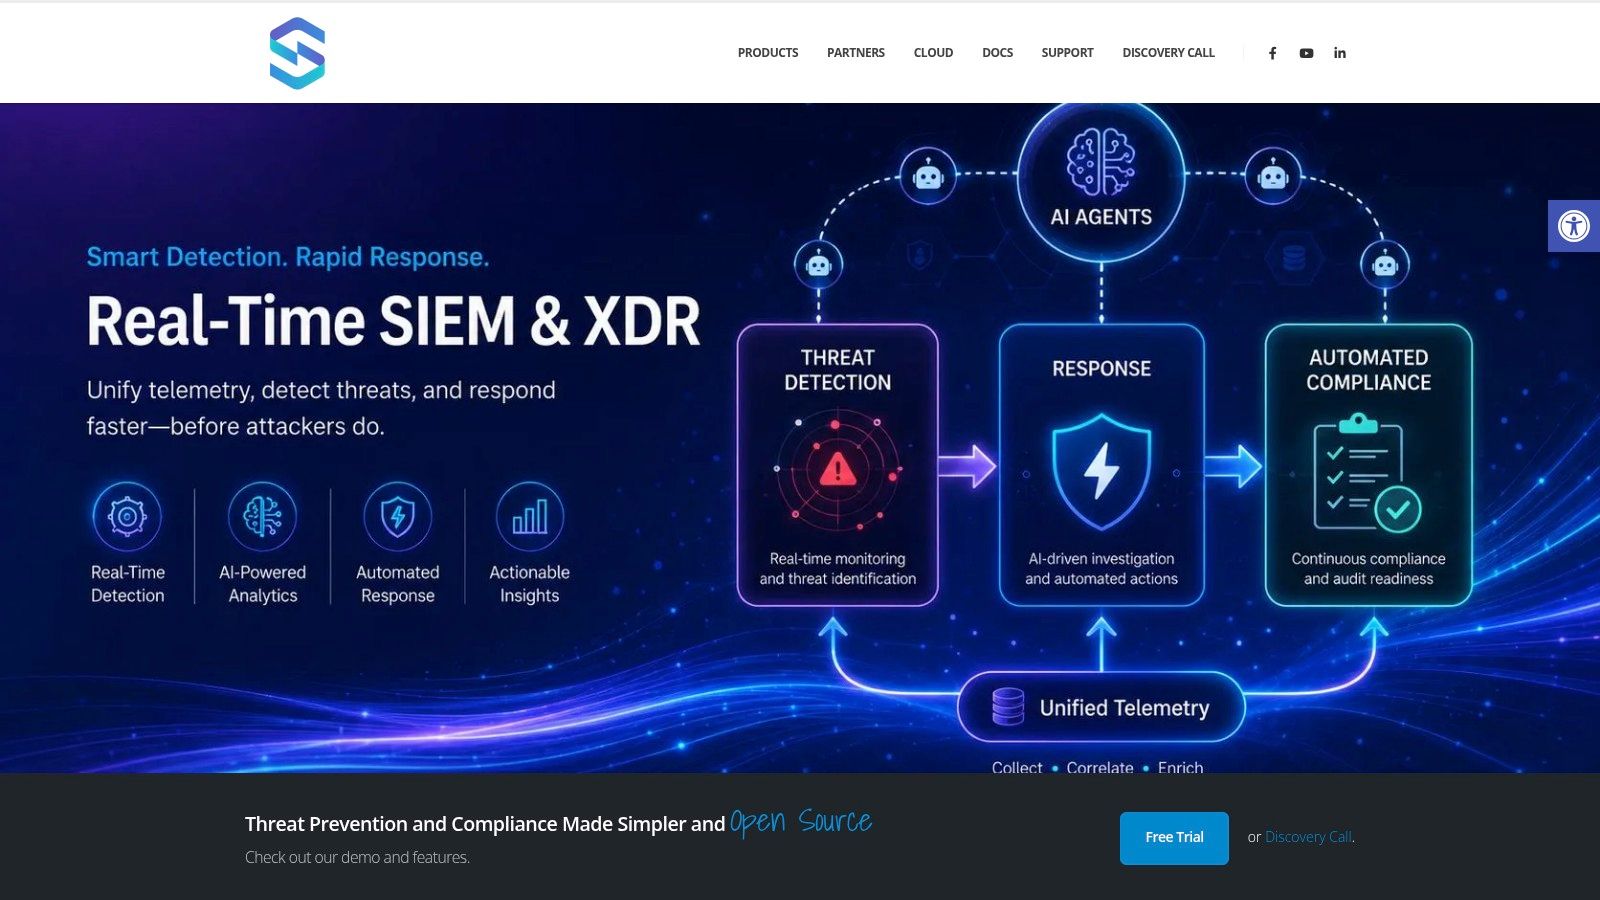
For teams evaluating platforms that combine these workflows, threat detection and response solutions should be evaluated by practical mechanics: ingestion, normalization, real-time correlation, case management, and whether analysts can adjust logic without opening three different products. Unified Security Stack is one example, an open-source SIEM, SOAR, and XDR platform that correlates telemetry and intelligence within a single workflow.
How SOAR and XDR turn context into action
After intelligence enriches an alert, SOAR should determine whether the case meets the bar for automation. That does not mean every hit should cause containment. It means the workflow should recognize when context is strong enough to lower hesitation.
Common examples include:
- Endpoint containment: Isolate a host when an observed artifact matches a trusted malicious indicator and endpoint behavior backs the finding.
- Network blocking: Move forward with a control change when multiple sources verify hostile infrastructure connected to current activity.
- Identity response: Require credential reset or session review when observed behavior corresponds to known credential abuse patterns.
- Compliance evidence capture: Keep alert context, analyst disposition, and response actions for frameworks such as HIPAA or PCI.
XDR adds another layer by connecting endpoint, identity, network, and cloud signals into a single investigation. Analysts no longer need to move between tools to determine whether a suspicious file event, a login anomaly, and outbound network activity are related.
Here's where seeing the workflow helps:
Analyst habit that works: Use intelligence as a scoring input for decisions, not as a replacement for validation. High-confidence context should accelerate triage, not remove it.
The usual failure point is over-automation supported by weak inputs. Ingesting noisy intelligence and wiring it straight into blocking actions produces outages, analyst distrust, and rollback work. Effective programs verify sources, assign confidence, and keep enrichment-only feeds separate from feeds eligible for automation.
Measuring the ROI of a Threat Intelligence Program
Security leaders do not need another abstract case for better context. What they must know is whether a threat intelligence program improves operations, refines risk decisions, and aids audit readiness.
What value looks like for security leaders
For a CISO, ROI frequently appears as stronger prioritization. Rather than spreading budget evenly across tools, the organization can align logging, detection engineering, and response workflows with the threats that matter most to its assets and industry.
To SOC managers, the payoff is nearer term. AWS notes in its threat intelligence overview that integrating CTI into security architecture reduces mean time to respond (MTTR) by enabling quicker detection and more robust response actions via correlation of data points including attacker intent and infrastructure. That claim aligns with what seasoned teams typically witness in practice: the analyst who starts with context resolves a case sooner than the analyst who begins from nothing.
For compliance leads, the return is reporting that can withstand scrutiny. Alerts supported by intelligence can demonstrate why a case was escalated, what artifacts mattered, and what control actions occurred. That context is important in audits because simply having an alert trigger is weaker evidence than an alert that triggered, was enriched, investigated, and tied to a documented response process.
Metrics that actually help
Not every metric deserves tracking. Measure what alters decisions or labor.
A practical scorecard often includes:
- Detection usefulness: How many alerts generated by intelligence were confirmed, escalated, or tuned out after review.
- Triage efficiency: Whether analysts decided cases faster when alerts arrived already enriched.
- Rule quality: Which correlation rules became stronger once TTP context was added instead of depending only on static indicators.
- Response consistency: Whether playbooks ran more dependably when cases included intelligence confidence and enrichment.
- Audit readiness: Whether incident records now hold sufficient context to back HIPAA, PCI, GLBA, or ISO control narratives.
If the only KPI you track is the number of feeds ingested, you are measuring input volume, not security value.
MSPs and MSSPs have an additional angle. Threat intelligence helps them offer proactive monitoring, higher-fidelity detections, and improved compliance reporting as a managed service outcome instead of a bundle of disconnected alerts.
How to Build Your Threat Intelligence Program
Creating a TI program from the ground up does not demand a massive team. It demands discipline. The most common early error is purchasing feeds before use cases are defined.
Start with requirements, not feeds
Start with a brief list of intelligence requirements linked to business risk. Determine which applications, identities, regulated data sets, subsidiaries, and third parties matter most. Then connect those priorities to operational questions your team must answer.
A practical starting sequence looks like this:
- Define protected assets: Identify the systems and data sets that would pose the greatest operational or compliance problem if compromised.
- Choose initial use cases: Choose a handful of specific outcomes, for example phishing detection enrichment, ransomware-related endpoint triage, identity abuse detection, or vulnerability prioritization.
- Map consumers: Determine the output each audience requires. Executives need risk statements. Analysts need artifacts and context. Engineers need detection logic.
- Limit source sprawl: Begin with a selected set of internal telemetry and a manageable group of external intelligence sources.
- Create disposition rules: Determine which data serves only as enrichment, which may affect scoring, and which is reliable enough to drive automated action.
This keeps the program connected to operations. It also avoids the frequent pitfall of collecting wide-ranging OSINT without ever converting it into detection content or investigation context.
Build the feedback loop into operations
How sources are integrated is as important as how good those sources are. ZeroFox characterizes an effective model as “bidirectional data flow” where validated intelligence goes to the SIEM for alerting, and SIEM events return to the threat intelligence platform for correlation and enrichment in its discussion of integrating threat intelligence with SIEM.
That principle ought to guide your architecture from the outset. Intelligence should not flow in just one direction.
What this looks like in practice:
- Inbound flow: Refined indicators, threat actor context, and TTP mappings add depth to detections and investigations.
- Outbound flow: Verified incidents, false positives, analyst annotations, and observed artifacts are returned to the intelligence process.
- Closed-loop tuning: Detection engineers adjust rules according to events seen in production.
- Reporting reuse: The workflow that adds context to a case should likewise retain evidence for compliance review.
Several implementation trade-offs deserve to be stated plainly.
First, open-source and community intelligence may prove valuable, yet only after you validate and normalize it prior to use in automated controls. Second, a single integrated platform tends to be simpler to govern than multiple loosely connected point products, particularly when the SOC and compliance teams require the same evidence trail. Third, technical intelligence is the simplest starting point, but the program gains durability once tactical and operational outputs start shaping detection engineering and response playbooks.
The strongest early milestone isn't “we have a lot of intel.” It's “our detections, investigations, and reports improved because intelligence changed how we work.”
Conclusion Intelligence Is Your Proactive Edge
Threat intelligence provides security teams with something they seldom have in sufficient supply: actionable context. It is not general awareness. It is not a heap of isolated indicators. It is practical, evidence-based knowledge that helps the SOC determine what is important, helps engineers adjust detections, and helps compliance teams explain what occurred and why.
That is what threat intelligence means in operational terms. It is the practice that converts dispersed telemetry, actor behavior, indicators, and threat reporting into action within SIEM, SOAR, and XDR workflows.
The four levels are important because distinct roles require distinct outputs. The lifecycle is important because intelligence quality rests on process, not volume. Activation within the security stack is important because intelligence demonstrates its value only when it alters detection, response, and reporting.
Organizations that omit this discipline remain reactive. They spend effort on excessive noise, automate the wrong activities, and find it difficult to link incidents to business risk or compliance evidence.
Organizations that build it effectively act differently. They set priorities more effectively, detect with greater context, respond more quickly, and document outcomes with less effort. In a modern security program, intelligence is not a secondary feed. It is the layer that helps every other control make stronger decisions.
If you're trying to operationalize threat intelligence in one place, Unified Security Stack merits consideration as an open-source SIEM, SOAR, and XDR platform that unites real-time detection, automated response, and compliance workflows within a unified stack.