What Is an XDR How It Works and Why It Matters
Your SOC dashboard is crowded. A suspicious process tree appears in the endpoint console. A phishing message is flagged by the email gateway. An unusual login is reported by your identity tool. At the same time, a cloud workload begins opening connections no one anticipated. Every alert could be important. Yet none of them, by itself, conveys the full picture.
That's the point where many security teams stall. They have invested in capable tools, yet those tools continue to act as distinct witnesses in one investigation. One observes the laptop. Another observes the mailbox. Another observes the account. The analyst must piece the incident together manually while the attacker continues to advance.
If you've been asking what is an XDR, in practical terms, the answer is straightforward. It is a method built to link those dispersed clues so your team can detect and respond as a single unit rather than through five separate consoles.
Table of Contents
- Introduction and Core Concepts of XDR
- XDR Architecture and Data Sources
- Comparing XDR with EDR SIEM and NDR
- Benefits and Limitations of XDR
- Real-World Use Cases in Hybrid Environments
- Implementation Guidance and Success Metrics
- Compliance Considerations and Vendor Evaluation
- Conclusion and Next Steps
Introduction and Core Concepts of XDR
A frequent SOC shortcoming is not inadequate tooling. It is insufficient connection among tools. An analyst observes malware activity on an endpoint, yet the network team has its own view of outbound traffic, the identity team keeps separate logs for account misuse, and the email team maintains a distinct phishing queue. If no one correlates those signals quickly, a minor alert grows into a wide incident.
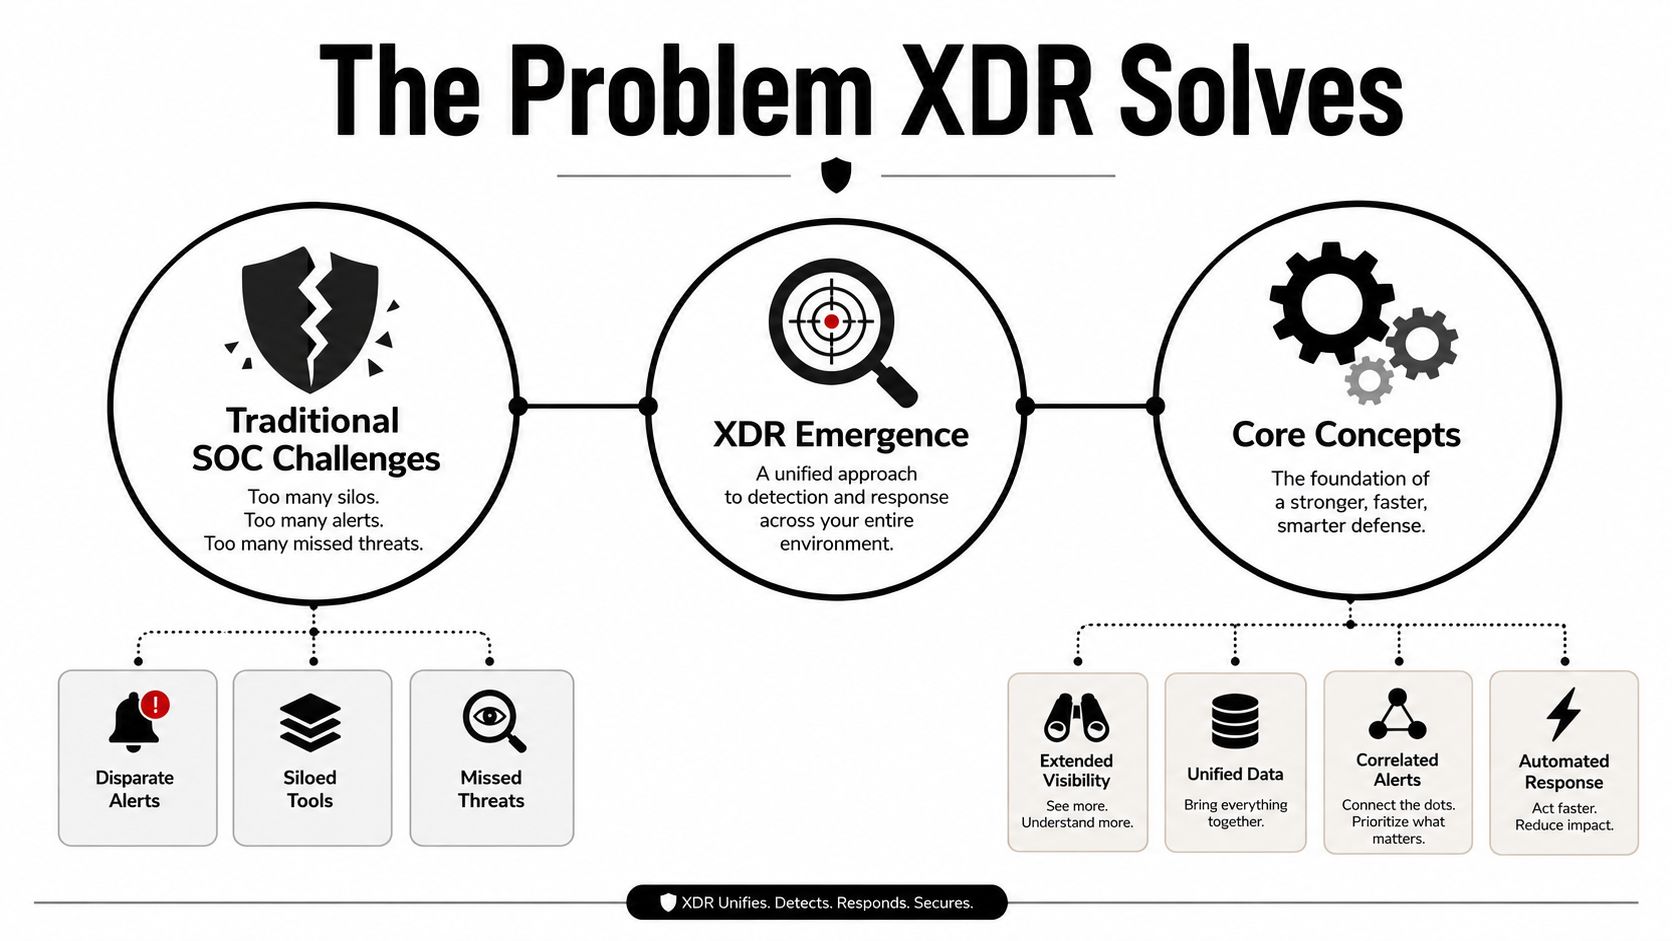
XDR stands for Extended Detection and Response. Gartner defines it as a SaaS-based, vendor-specific security platform that natively integrates multiple security products into a cohesive operations system, shifting security from siloed tools to a holistic view across the technology stack, as described in Google Cloud's XDR overview.
That definition may seem abstract, so translating it into everyday language can help. XDR gathers telemetry from sources including endpoint detection, network visibility, email security, identity systems, and cloud security controls. It then correlates those signals so a SOC analyst sees a single incident narrative rather than a heap of disconnected alerts.
Why teams ask for XDR in the first place
Picture EDR as a camera aimed at the laptop. Helpful, yet limited. XDR is more like a control room that brings in camera feeds, badge-reader logs, mailroom records, and hallway motion sensors, then indicates which events belong to the same break-in.
Practical rule: If your analysts spend more time switching between consoles than confirming attacker behavior, you do not merely have a detection issue. You have a context issue.
For teams exploring threat detection and response platforms, that context is a central pledge. XDR seeks to shorten threat dwell time, enhance visibility, and coordinate response actions from one central location rather than requiring the SOC to manually reconcile every clue.
XDR Architecture and Data Sources
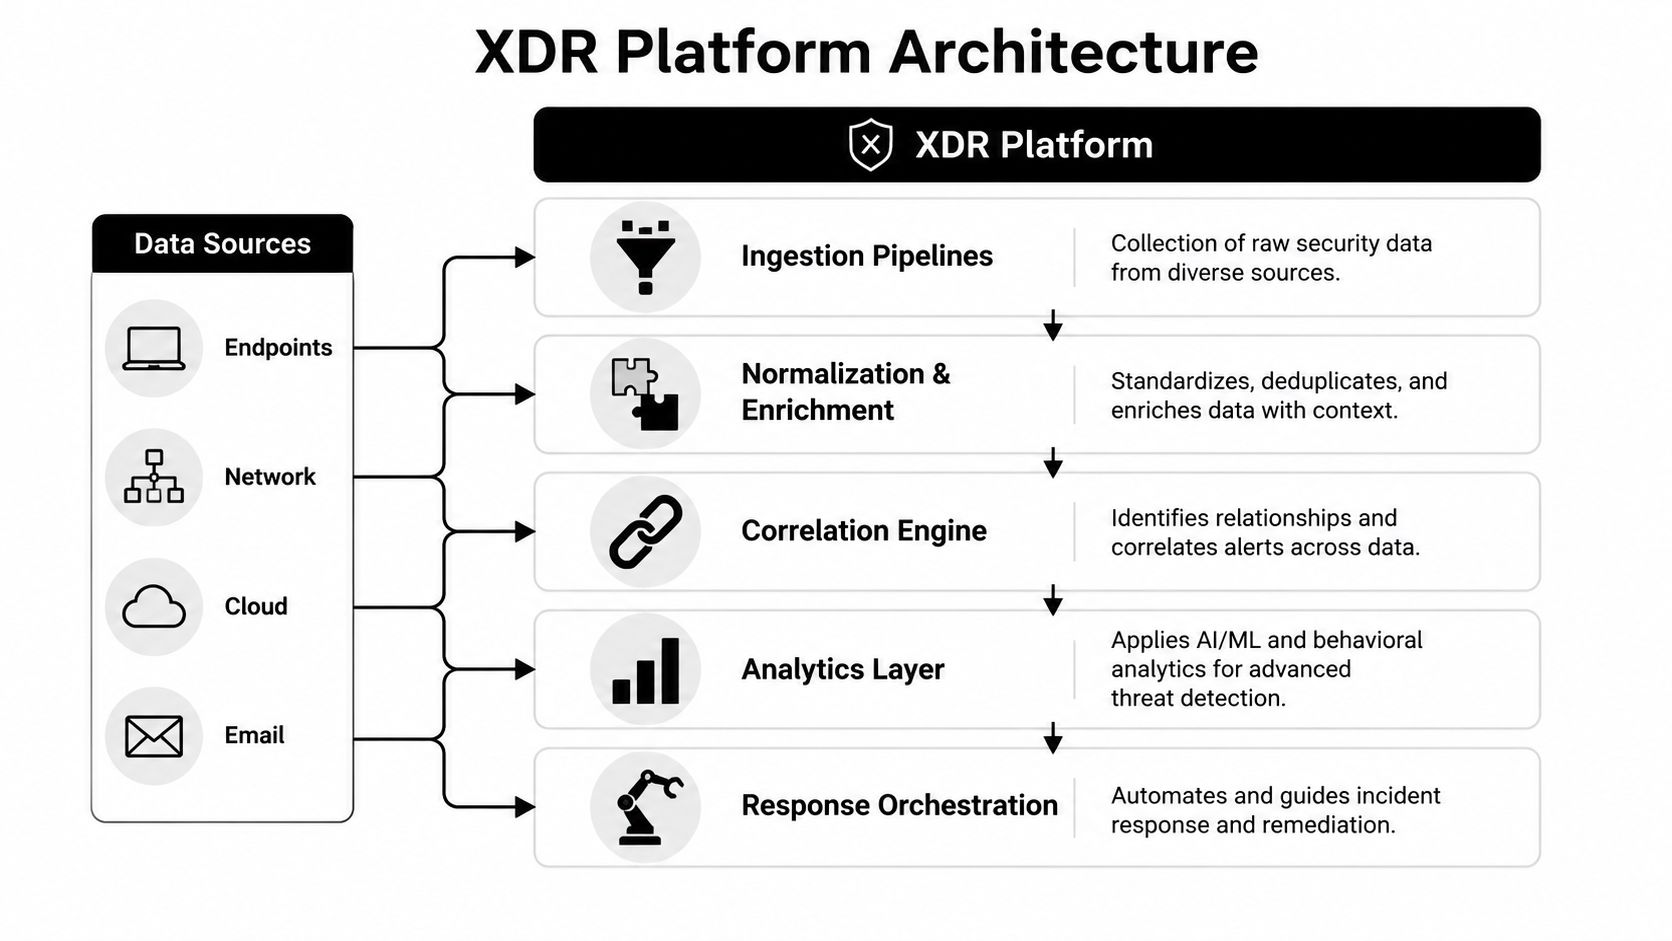
XDR functions by treating security data as a pipeline rather than a pile. Raw events arrive from various parts of the environment, are cleaned and enriched, then move through correlation and analytics before response actions trigger. If any single stage is weak, the platform turns noisy or blind.
Why telemetry fusion matters
A phishing campaign offers a straightforward example. The email layer observes a suspicious attachment. The identity system detects a login from an unusual pattern. The endpoint agent identifies script execution. The network layer sees lateral movement. Separate tools generate separate alerts. XDR attempts to recognize them as a single attack chain.
Expert analysis notes that XDR often combines concepts such as Network Traffic Analysis (NTA), Network Intrusion Detection Systems (NIDS), and Network Intrusion Prevention Systems (NIPS) to give SOC teams more context while using AI to analyze aggregated logs and alerts in real time, according to the Wikipedia entry on Extended Detection and Response.
Later in the workflow, the architecture is easier to picture as a series of stages rather than one feature.
The main layers inside an XDR platform
Ingestion pipelines
Data comes in from endpoint agents, API integrations, Syslog feeds, cloud platforms, email gateways, and identity providers. In hybrid environments, this is important because one part of an attack may begin in SaaS while another lands on an on premises host.Normalization and enrichment
Raw records arrive in inconsistent formats. A user may be identified by email address from one source, by username from another, and by internal ID from a third. XDR normalizes these fields and adds context, including asset role, user privilege, and threat intelligence tags.Correlation engine
The platform connects events that would appear harmless on their own. A failed login, a mailbox rule change, and a script launch could be unrelated. Or they might represent the same intrusion path.Analytics layer
This layer searches for patterns, anomalies, and attack sequences that simple rule matching may overlook. It is particularly useful for dormant malware, internal reconnaissance, and lateral movement that spans more than one domain.Response orchestration
When confidence is sufficient, the platform can guide or automate actions including isolating an endpoint, disabling an account, blocking a sender, or opening an incident with the appropriate context attached.
XDR is not a single magic detector. It is a system that converts different security signals into one investigation workflow.
Comparing XDR with EDR SIEM and NDR
Security leaders frequently compare XDR with EDR and ask whether it is merely a rebrand. It is not. The more valuable question is what each tool is designed to observe, and what each one overlooks when it operates alone.
Where each tool fits
EDR concentrates on endpoints. It monitors processes, files, scripts, persistence techniques, and local response actions. It performs well when malware resides on a host, but on its own it will not provide full visibility into email-borne compromise, identity abuse, or cloud control-plane activity.
SIEM collects and stores logs from numerous systems. It is useful for investigations, detections, and compliance reporting, particularly when teams require long-term searchability across servers, applications, firewalls, and identity tools. However, a SIEM often relies on the SOC to build and tune the logic that connects events in a meaningful way.
NDR monitors the network. It helps detect command-and-control traffic, lateral movement, beaconing, and unusual east-west communications. However, NDR may have difficulty identifying who started the activity, which mailbox began the chain, or what process triggered it on the host.
XDR spans those layers. Its purpose is not so much to replace each product category entirely but to provide the SOC with a shared location for correlation and response.
For organizations already evaluating endpoint protection platformsThis distinction is important. Purchasing robust endpoint tools does not by itself resolve cross-domain investigations.
Feature Comparison of XDR EDR SIEM and NDR
| Solution | Detection Scope | Key Data Sources | Response Automation |
|---|---|---|---|
| XDR | Cross-layer detection across multiple security domains | Endpoints, network, email, identity, cloud workloads | Centralized and often guided or automated across connected controls |
| EDR | Endpoint-focused activity and compromise | Endpoint agents, process events, file activity, registry and script behavior | Strong on host isolation and local containment |
| SIEM | Broad log aggregation and analytics | Logs from infrastructure, applications, security devices, identity systems | Usually depends on integrations, rules, and external orchestration |
| NDR | Network-centric threat detection | Network traffic, flow records, packet-derived metadata, sensor output | Usually focused on network actions and analyst-driven investigation |
When malware on laptops is your primary problem, EDR can be sufficient. When your problem involves attack chains spanning email, identity, cloud, and endpoint layers, XDR is the stronger choice.
Benefits and Limitations of XDR
The strongest case for XDR is operational clarity. Rather than requiring analysts to manually piece together alerts from separate product silos, it provides a single incident view. This alters the experience of triage in practice. Analysts spend less effort gathering evidence and more effort determining what to contain first.
What teams gain
A key reason this category draws interest is that many leaders recognize their need for it, even without a precise definition. XDR is recognized as a necessity by 78% of IT leaders, yet only 47% can correctly identify its true definitionThis is based on ExtraHop findings reported by Business Wire.
That gap is significant because teams may buy an XDR offering expecting a full SOC operating layer, only to get something closer to broader endpoint tooling. A vague definition leads to a vague project scope as well.
Common benefits include:
- Broader context: incidents are easier to comprehend because signals from endpoint, network, email, identity, and cloud are assessed as a whole.
- Faster prioritization: the SOC can prioritize incidents according to a more complete attack chain instead of one kind of alert.
- More consistent response: teams can standardize actions so the same incident category is managed consistently.
Where teams still struggle
The constraints matter equally.
- Vendor lock-in: a lot of XDR solutions rely on native integration with the vendor's own product set.
- Third-party gaps: when a tool claims open integration, the extent of that integration can still vary.
- Rule quality: inadequate tuning can still overwhelm analysts with noise, particularly in the initial deployment phase.
- Expectation mismatch: some buyers believe XDR removes the requirement for SIEM, NDR, or detection engineering. Typically, it does not.
Purchasing XDR does not eliminate the need for sound telemetry hygiene. If the platform takes in poor, incomplete, or badly mapped data, it will accelerate confusion through automation.
Real-World Use Cases in Hybrid Environments
An effective XDR deployment demonstrates its worth in complex environments. Most organizations are neither fully cloud nor fully on-premises. They operate remote endpoints, SaaS applications, private infrastructure, identity providers, email services, and a blend of security products accumulated over time. That is where XDR becomes practical rather than theoretical.
Lateral movement across cloud and on premises systems
An attacker breaches a workstation via a script-based payload. The endpoint agent detects suspicious execution, yet the first major indicator emerges elsewhere. The network layer begins to see internal discovery activity, and a cloud workload records unusual access attempts from the same user context.
Without XDR, those alerts might remain in separate queues. With XDR, the system can tie the user, host, network path, and cloud activity together into a single incident. The analyst sees a probable lateral movement sequence rather than four medium-priority alerts.
A SOC team can then isolate the host, examine identity misuse, and review affected workloads within one workflow.
Phishing that spreads from inbox to identity to endpoint
A user gets a credible message that slips past basic filtering. After delivery, the email gateway marks suspicious traits. Shortly afterward, the identity provider logs unusual authentication activity, and the endpoint reveals a fresh browser download followed by script execution.
This forms a typical multi-vector chain. Email by itself does not prove compromise. Identity by itself can resemble user mistake. Endpoint by itself can resemble commodity malware. XDR links the sequence and informs the SOC that the mailbox, account, and device belong to one incident.
A compelling XDR use case is not about collecting more alerts in one location. It is about having fewer separate explanations for the same attacker behavior.
Remote workforce investigations without swivel-chair analysis
Across distributed organizations, the network perimeter no longer provides the full picture. Users work from home, reach SaaS directly, and shift between managed and semi-managed environments. Analysts must see what occurred on the endpoint, within the identity system, and inside cloud applications without physically handling the device.
XDR assists by bringing those signals into a single investigative view. The SOC can examine timeline data, verify whether the same user caused related events, and start containment actions even if the affected employee is away from the office.
Teams often first recognize the value during practice. This happens not because attacks are more unusual, but because the environment is more fragmented.
Implementation Guidance and Success Metrics
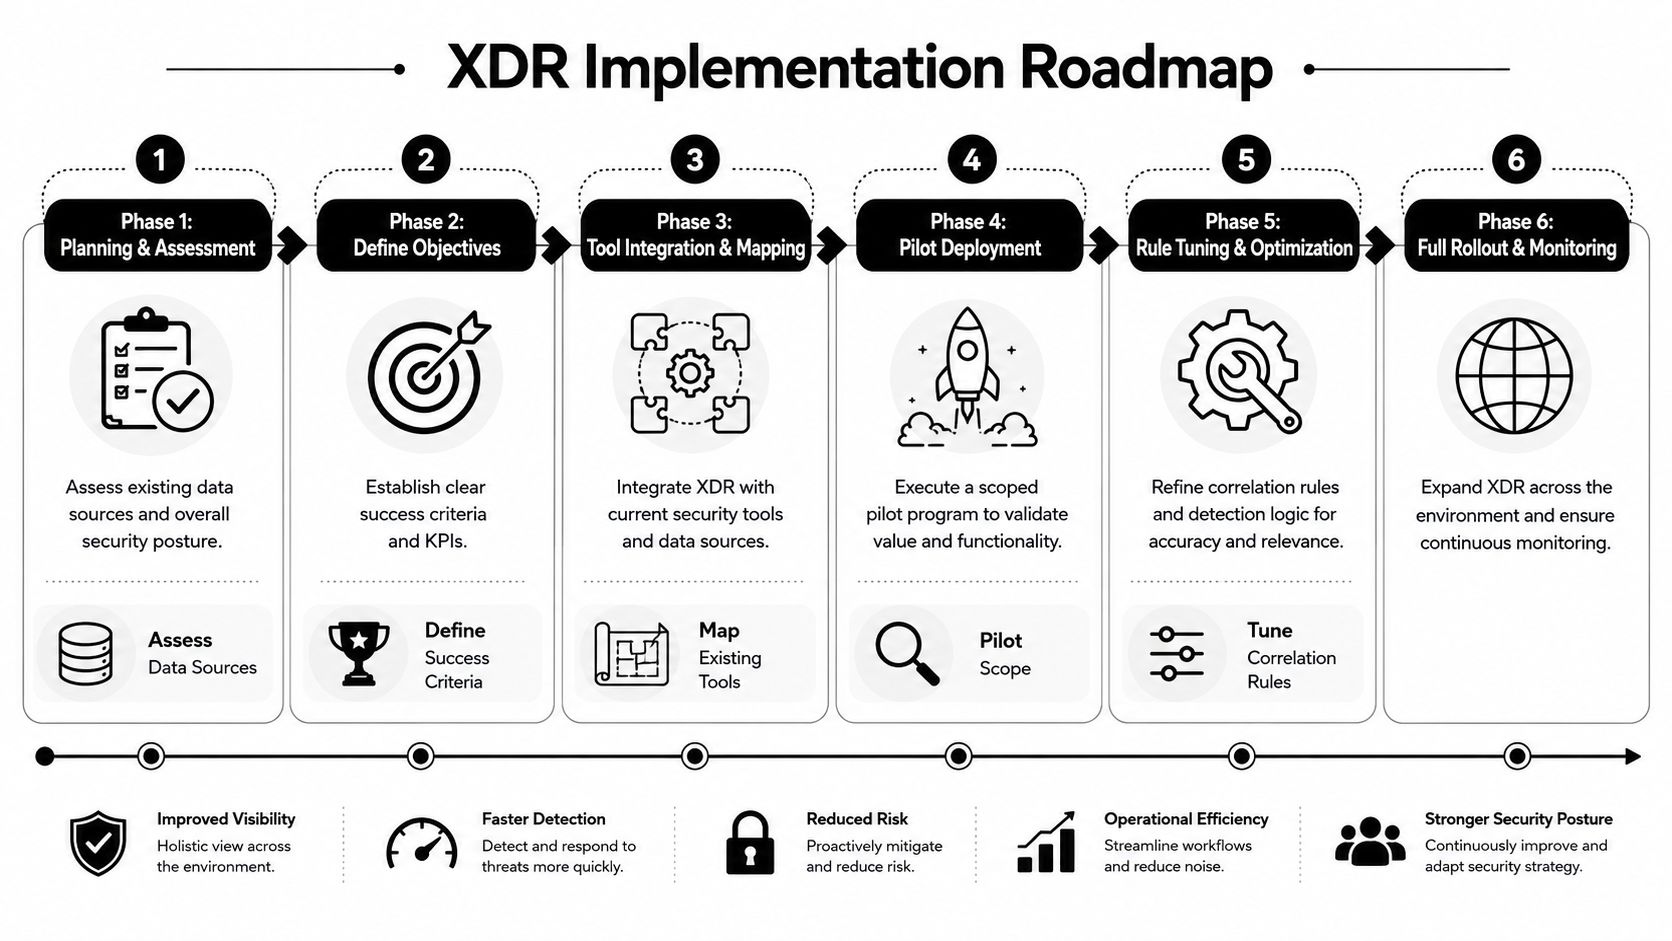
XDR deployment goes more smoothly when the team approaches it as an operational design effort, not merely a product installation. Begin with your existing telemetry map. Which systems currently produce useful security events, and which remain blind spots? Most unsuccessful deployments occur because the organization first connects whatever is simplest rather than what best explains attacker behavior.
A practical rollout sequence
A workable sequence usually looks like this:
Inventory the data sources that matter most
Concentrate on endpoint telemetry, identity events, email signals, cloud audit trails, and network visibility. Do not pursue every source at the same time.Pick a narrow pilot scope
Choose a single business unit, one cloud environment, or one attack path like phishing-to-endpoint compromise. A targeted pilot exposes tuning issues early.Map fields across tools
Ensure usernames, device identifiers, and asset tags align. Correlation breaks when the same entity shows up under different labels.Tune detections with analysts in the loop
The people who handle incidents every day should review initial rules. They will identify duplicate logic, poor thresholds, and absent enrichment faster than any procurement checklist.Define response playbooks before rollout expands
Determine which actions are automatic, which require analyst approval, and which always demand escalation.
What to measure after deployment
Exotic metrics are not necessary. You need metrics that the SOC can apply.
- Mean time to detect: Is the team identifying suspicious activity sooner in the attack chain?
- Mean time to respond: Once incidents are confirmed, are containment actions occurring more quickly?
- Alert volume trend: Is correlation cutting down on duplicate cases across tools?
- False-positive ratio: Are analysts devoting less time to dismissing noise?
- Coverage by data source: Which critical domains still are not sending data to the platform?
For teams that want a modular route rather than a closed stack, Unified Security Stack One option worth assessing merges SIEM, SOAR, and XDR capabilities within an open-source architecture and collects data via APIs, Syslog, NetFlow, and agents while enabling rule tuning and response orchestration.
Compliance Considerations and Vendor Evaluation
Security teams in regulated settings seldom purchase detection tools only for detection. They also require evidence, log retention, access visibility, incident records, and reports aligned with frameworks such as HIPAA, PCI, CMMC, ISO 27001, and GLBA. XDR is valuable when it can link technical events to users, systems, and response actions in a manner auditors can trace.
How XDR supports compliance work
Combined telemetry strengthens compliance efforts because controls do not fail in tidy categories. A PCI incident can include endpoint activity, account abuse, firewall logs, and cloud service events. A HIPAA investigation may need to connect user behavior, workload access, and alert timelines. XDR enables that workflow by keeping detections and responses linked to one case narrative.
Open and modular architectures also merit greater consideration here. Most XDR articles ignore modular open-source architectures, yet 78% of mid-market SOC teams cite alert fatigue from disconnected tools as their top pain point, creating a decision gap for cost-constrained organizations seeking unified SIEM and XDR, as noted in CrowdStrike's XDR overview.
If your team is comparing proprietary suites with more flexible designs, centralized log management capabilities belongs in the evaluation rather than being an afterthought. Compliance evidence typically depends on how well logs are gathered, normalized, retained, and tied to investigations.
Questions to ask before you buy or build
Ask vendors, or your internal platform team, direct questions:
- To what extent is the ingestion layer open? Is it able to ingest APIs, Syslog, NetFlow, and agent data without requiring a complete product swap?
- To what extent is correlation customizable? Are analysts allowed to create and adjust rules for your environment, rather than relying only on vendor defaults?
- What is mapped by compliance reporting? Seek workflows tied to evidence, not merely generic dashboards.
- How much context remains in the case record? Both auditors and incident responders require timelines they can trace.
- What is the cost of operations? License fees matter, but so do headcount burden, integration upkeep, and clearing alert noise.
Open-source XDR is not inherently superior to proprietary XDR. Still, for certain teams, it remains the only practical route to broad telemetry fusion without increasing license sprawl.
Conclusion and Next Steps
The best way to view XDR is not as yet another dashboard category, but as an answer to a genuine SOC challenge. Attackers do not remain in a single layer, and your defenders cannot afford to investigate within one layer either. When endpoint, identity, email, network, and cloud activity stay siloed, analysts waste time when they can least afford to.
If you are still asking what an XDR is, pose a tougher follow-up. Does your existing stack enable the SOC to present one coherent incident story, or does it make people rebuild that story manually?
Begin by auditing your current telemetry, alert flows, and response playbooks. Determine the areas where incidents often split across tools. Next, conduct a pilot that evaluates correlation quality, analyst workflow, and evidence capture. For many teams, the correct choice will not be to purchase the largest suite. It will be selecting the model, proprietary or open-source, that suits their environment, staffing, compliance duties, and integration realities best.
If you're evaluating a unified approach to SIEM, SOAR, XDR, and compliance reporting, Unified Security Stack merits a closer look. It delivers an open-source platform for centralized telemetry, real-time correlation, automated response, and compliance workflows across hybrid environments.