Top Vulnerability Scanner Tools Open Source 2026
Executing a vulnerability scan is straightforward. The challenge begins when your backlog overflows with redundant findings, obsolete CVEs, and reports that fail to identify what is actually exposed in production. If you aim to construct a functional vulnerability scanner tools open source architecture in 2026, the critical issue is not which scanner is available, but which one aligns with your environment and integrates seamlessly into your SIEM/XDR pipeline to help you prioritize significant risks. This distinction is vital when you require audit-ready evidence for HIPAA, CMMC, or PCI, since raw results rarely match the workflows of security teams, auditors, and incident responders.
For teams that want one place to correlate scanner output with logs, assets, and response actions, a platform like VolunteerBadge can help clarify the operational challenge. Top-tier open-source scanners still require context, normalization, and triage to become effective within a SOC. Consequently, the tools listed below are evaluated not merely on detection breadth, but on their behavior once their output enters a centralized security program.
Table of Contents
- 1. Vulnerability Scanner for Unified Security Stack
- 2. OpenVAS/GVM from Greenbone Community Edition
- 3. Zed Attack Proxy (OWASP ZAP)
- 4. Nikto
- 5. OpenSCAP
- 6. Lynis by CISOfy
- 7. Trivy
- 8. Grype by Anchore
- 9. Clair
- 10. Vuls
- Top 10 Open-Source Vulnerability Scanners, Feature Comparison
- Making Your Selection A Strategic Approach
1. Vulnerability Scanner for Unified Security Stack
Unified Security Stack's vulnerability scanner is the strongest choice here if your real problem is not scanning, but turning scan data into response. It resides within the Unified Security Stack SIEM/XDR platform, ensuring findings are not isolated in a separate console. They can be correlated with logs, alerts, assets, and playbooks, distinguishing between “we identified a CVE” and “we understand where it matters.” The platform also links findings to compliance workflows, simplifying evidence generation for regulated environments.
The scanner combines Nuclei templates, the CVE Binary Tool, and OSV data, offering a practical balance of network checks, binary analysis, and software supply-chain visibility. This combination is crucial because many teams require coverage across endpoints, packages, and artifacts, rather than just a single scan surface. Unified Security Stack supports both network and agent-based scans, along with configurable templates, targeted runs, and scheduling. For a SOC, this allows findings to be timed, filtered, and routed rather than dumped into a generic report.
Practical rule: if a scanner cannot place findings alongside your alerts and response actions, you will spend more time on triage than remediation.
A significant advantage lies in how Unified Security Stack manages downstream tasks. Correlation and LLM-assisted triage help diminish noise, while SOAR playbooks can automate containment when a finding relates to active risk. In a SIEM/XDR context, this is more valuable than another standalone scanner because it accelerates the transition from detection to action. It is also the most seamless fit if you require a unified workflow for HIPAA, PCI, or ISO 27001 reporting.
The compromise is operational. Open-source engines still demand template tuning, and agent-based scanning introduces endpoint deployment overhead. However, for teams already seeking centralized visibility, this trade-off is typically justified.
Best fit: security teams seeking vulnerability intelligence within the same platform they use for detection, correlation, and response.
Website: Unified Security Stack Vulnerability Scanner documentation
Internal reference: Unified Security Stack vulnerability scanning tools
Image: 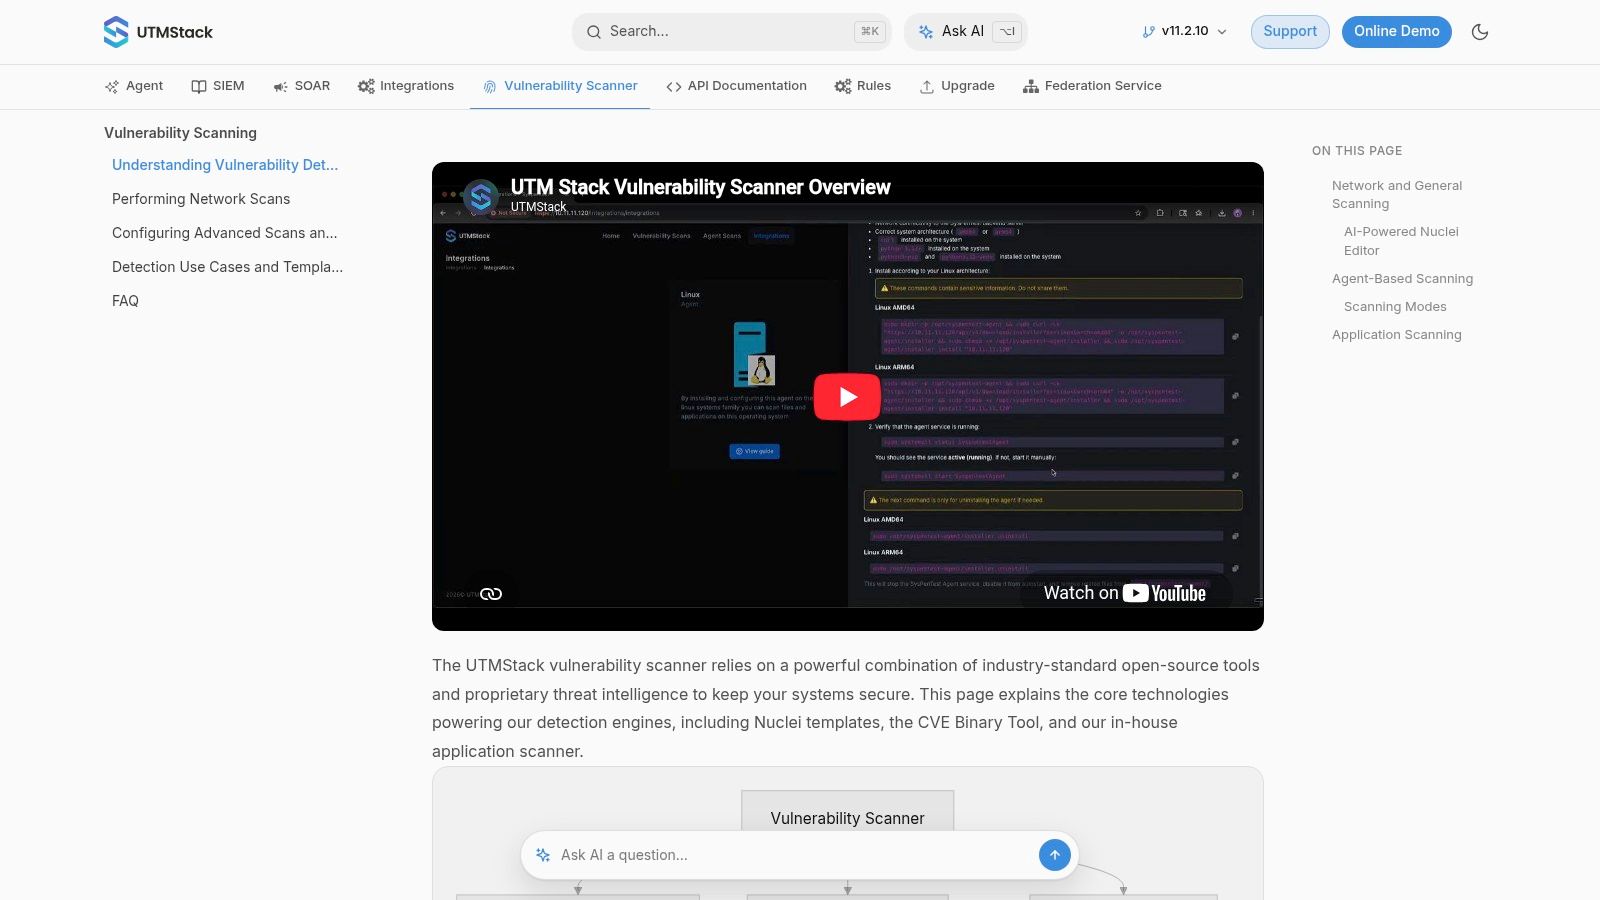
2. OpenVAS/GVM from Greenbone Community Edition
Greenbone Community Edition is still the default answer when a team asks for a mature network vulnerability management architecture. The German Federal Office for Information Security notes that Greenbone AG has been the primary developer since 2006, and that BSI supported its development, explaining why OpenVAS is regarded as a baseline reference in this category. This heritage is practically important because network teams often prefer tools with a long history, known behavior, and a clear upgrade path.
Greenbone’s utility stems from its breadth. It supports authenticated and unauthenticated scans, scheduling, reporting, and automation via APIs and GVM command-line tools. For routine infrastructure assessments, this makes it far easier to operationalize than a one-off scanner. It is particularly valuable when you need repeatable checks across subnets, exposed services, or internet-facing assets.
Practical rule: use Greenbone when your priority is infrastructure coverage, rather than web-app fuzzing or container artifact scanning.
There is also a governance aspect. The platform’s community and enterprise feeds provide a pathway from free scanning to supported operations, which is significant if you eventually require more predictable content maintenance. The drawback is equally evident. Community coverage will not match enterprise feed depth, and organizations relying on commercial appliances or keys will need to budget for that subsequently.
For SIEM/XDR teams, the primary benefit is that Greenbone findings are structured sufficiently for ingestion and correlation. This is where tools like Unified Security Stack become relevant, as a network finding is only valuable when linked to asset identity, logs, and change history. Lacking that context, you encounter scan noise. With it, you achieve prioritization.
Website: Greenbone Community Edition documentation
Reference context: BSI's OpenVAS background
Image: 
3. Zed Attack Proxy (OWASP ZAP)
OWASP ZAP is the tool I reach for when the question is, “What can an attacker do against the running app or API right now?” It's a DAST tool initially, making it much better suited for web applications and APIs than infrastructure scanning. It functions as an intercepting proxy, supports active and passive scanning, and offers sufficient automation support to integrate into CI/CD without becoming a manual-only pentest tool.
This CI/CD integration is what makes ZAP valuable for modern delivery teams. You can execute it headless, integrate it through APIs, and deploy it against staging environments where authentication, session handling, and actual application behavior are critical. The tool’s add-on ecosystem is also a practical benefit, allowing teams to extend coverage without replacing the core workflow.
One caution is essential. Active scanning can strain fragile targets, so ZAP should be used in controlled environments where breakage will not disrupt production. It is also unsuitable for OS packages, container images, or dependency inventories. These gaps are typical for DAST, but they are significant if someone expects a single scanner to cover everything.
Practical rule: ZAP addresses runtime exposure, not package CVEs or server misconfigurations outside the application layer.
From a SIEM/XDR standpoint, ZAP findings become significantly more useful when correlated with authentication logs, API gateway data, and endpoint telemetry. This is where a centralized platform delivers value. A reflected input issue is interesting in isolation. A reflected input issue linked to a real user session, an internet-facing endpoint, and suspicious activity in logs constitutes a priority incident.
Website: OWASP ZAP
Image: 
4. Nikto
Nikto is direct, fast, and remains useful because it does not claim to be a comprehensive application scanner. It focuses on the web server layer, scanning for risky files, obsolete server components, and typical configuration errors. This makes it a good fit for rapid reconnaissance, baseline assessment, and scripted checks when you want a clear signal without a complex setup.
Its primary strength is usability. The signature database is pluggable, output formats are flexible, and it operates across IPv4 and IPv6 with proxy support. For teams conducting recurring hygiene scans, this is sufficient to catch obvious errors before they escalate into larger exposure. It also complements deeper tools like ZAP by identifying boring but critical server issues that DAST tools may not prioritize.
The constraint is just as clear. Nikto relies on signatures rather than acting as a full DAST engine. It cannot assess application logic, and without manual follow-up it gives little useful context about exploitability. As a result, findings usually need validation before they become tickets.
Nikto functions best as a lightweight triage utility for publicly accessible web servers. It effectively highlights clear misconfigurations, yet it should not serve as the sole tool in your web security arsenal.
Website: Nikto
Image: 
5. OpenSCAP
OpenSCAP stands out because it speaks the language of compliance and hardening, extending beyond simple vulnerability identification. It leverages SCAP standards like OVAL and XCCDF and includes the SCAP Workbench GUI alongside the oscap CLI, while integrating with the SCAP Security Guide for policy definitions such as PCI-DSS, DISA STIG, and CIS profiles. This makes it more suitable for standardized host evaluation than for extensive attack-surface mapping.
The real benefit lies in consistency. When your team must assess Linux hosts against established baselines, OpenSCAP provides a structured methodology. It proves particularly valuable when you require proof that a control has been evaluated, rather than simply confirming that a scan occurred. This distinction is critical for auditors.
Its primary limitation is also structural. OpenSCAP relies on up-to-date SCAP content, meaning that if the content is outdated, coverage suffers accordingly. Consequently, operational effectiveness hinges on feed maintenance and policy management, not merely on installing the software.
For security initiatives that must address both engineering and compliance requirements, OpenSCAP is a necessary addition to the stack. Within a SIEM/XDR workflow, its results hold the most value when linked to asset identity and compliance status, allowing you to differentiate between configuration drift and active exposure. If you require a centralized repository for this data, Unified Security Stack’s vulnerability management processes offer a better solution than another standalone dashboard.
Practical rule: use OpenSCAP when the question is “does this host meet policy?” not “what can an attacker exploit across the stack?”
Website: OpenSCAP
Internal reference: Unified Security Stack vulnerability scanning overview
Image:
6. Lynis by CISOfy
Lynis stands out as a highly practical tool for host hardening due to its exclusive focus on the operating system layer. Compatible with Linux, macOS, and Unix, it conducts thorough checks on services and configurations, offering specific hardening recommendations. This makes it ideal for fleet baselining, particularly for administrators seeking a lightweight and scriptable solution.
The tool’s appeal stems from its ease of repeated execution. You can integrate it into automation workflows, compare results across different systems, and identify weak default settings before they escalate into operational issues. The commercial Lynis Enterprise version offers centralized reporting and guidance, which is essential for larger environments requiring a unified management view instead of disparate local reports.
The constraint is scope. Lynis does not aim to function as an application vulnerability scanner and cannot replace tools that examine containers, web applications, or dependency graphs. This is not a defect but a deliberate design choice. For OS-level auditing, this focus is an advantage because it avoids overpromising capabilities.
Within a SIEM/XDR framework, Lynis findings are most impactful when associated with host identity, change events, and asset criticality. This transforms a hardening checklist into actionable data for SOC prioritization. In regulated industries, it also assists in demonstrating that baseline controls are consistently verified.
Website: Lynis by CISOfy
Image: 
7. Trivy
Trivy is one of the most versatile open-source scanners because it covers containers, filesystems, OS packages, SBOMs, IaC, and secrets. This breadth is precisely why it appears frequently in contemporary DevSecOps workflows. It suits developers, platform engineers, and security teams requiring a single scanner to examine multiple artifact types without adopting separate tools for each repository.
The OSV Scanner project illustrates the broader trend that tools like Trivy address, shifting from perimeter-only assessments to code and artifact validation. It scans SBOMs, lockfiles, directories, and container images, reflecting how significant vulnerability detection now occurs before workloads enter production. This is crucial for CI/CD pipelines, as earlier detection significantly reduces remediation costs.
Trivy’s operational advantage is its speed and flexibility. It integrates easily into pipelines and Kubernetes workflows, covering a wide attack surface without requiring a resource-intensive deployment model. The compromise is governance. The open-source version concentrates on scanning, whereas comprehensive enterprise workflow controls are available in commercial offerings.
Practical rule: use Trivy when your infrastructure includes containers, IaC, and source artifacts, and you require a single scanner that keeps pace with developer velocity.
For organizations operating a SIEM/XDR stack, Trivy findings gain greater value when normalized into the same asset and alert model used for infrastructure alerts. This enables you to distinguish between a vulnerable image that was never deployed and one currently running. Unified Security Stack is well-suited for this workflow as it centralizes vulnerability management alongside correlation and response capabilities.
Website: Trivy
Internal reference: Unified Security Stack vulnerability management tools
Image: 
8. Grype by Anchore
Grype is a clean fit for teams that want a CLI vulnerability scanner for container images and filesystems using SBOM-aware workflows. Anchore’s documentation indicates it can scan SBOMs, local filesystems, and images, which is significant because many teams now favor artifact-level scanning over rebuilding every image from scratch. It also integrates seamlessly with Syft, making it appealing for software supply-chain tasks.
The practical reason to favor Grype is its repeatability. It integrates smoothly into CI/CD, produces structured output, and functions in pipelines where deterministic scanning is preferred over a UI-driven experience. It is particularly beneficial when security and platform teams wish to generate an SBOM first and then scan it without repeating the entire artifact analysis.
Its limitation is focus. Grype targets known-vulnerability detection in packages and artifacts, excluding runtime web testing or extensive DAST. This narrow scope is acceptable if understood, but it implies that additional tools are necessary for APIs, web applications, and server checks.
Practical rule: Grype performs best when your software supply chain is already SBOM-aware and you seek scan results that are easily automated.
In a SIEM/XDR program, Grype output proves most useful when correlated with build metadata and deployment telemetry. This reveals whether a vulnerable image remained in CI, was blocked, or reached a runtime environment. For teams utilizing Unified Security Stack, this correlation step converts raw scanner output into actionable decision-making data.
Website: Grype documentation
Image: 
9. Clair
Clair is among the more infrastructure-oriented container scanners, functioning as a static analysis engine that indexes packages and matches them against distribution vulnerability feeds. It is frequently embedded within registries and CI systems, indicating it is designed for server-side scanning rather than interactive use.
This architecture makes Clair attractive to platform teams wanting scanning near the registry or build pipeline. The model is also transparent, as package indexing and source matching are explainable, which aids developers in understanding why a vulnerability was flagged. In practice, this reduces ambiguity during review and remediation.
The trade-off is scope. Clair concentrates on container and package CVEs, so it cannot replace DAST or host auditing tools. It serves as a solid component, not a comprehensive program.
For security teams constructing a broader control plane, Clair is most effective as one ingestion source among several. Container findings become significantly more actionable when aggregated with runtime logs, workload identity, and network exposure data within a SIEM/XDR platform. This approach shifts the perspective from “this image has a CVE” to “this deployed workload is the priority for remediation.”
Website: Clair
Image: 
10. Vuls
Vuls is the right kind of tool for teams that want agentless OS vulnerability scanning on Linux and FreeBSD. It connects via SSH or local-scan mode, lists installed packages, and compares them against NVD, OVAL, and vendor advisories. This makes it appealing for heterogeneous fleets where deploying an agent everywhere is undesirable just to achieve baseline package visibility.
The utility also supports historical tracking. Its reporting features and the optional VulsRepo viewer simplify reviewing findings over time, which assists in demonstrating progress or identifying recurring exposure across hosts. For administrators seeking automation without a heavy operational footprint, this represents a solid balance.
Its limitations are clear. It does not cover Windows and remains at the OS package layer rather than application behavior. Consequently, while Vuls is useful in host-risk workflows, it cannot assist with web applications, containers, or runtime exploit validation.
Practical rule: Vuls is most effective where SSH access is already part of your operational model and agent deployment would be burdensome.
Regarding SIEM/XDR integration, value is derived from incorporating Vuls findings into the same asset view as authentication, patching, and change records. This enables a SOC to distinguish between a vulnerability that is merely present and one residing on a system that is actively exposed or recently changed.
Website: Vuls
Image: 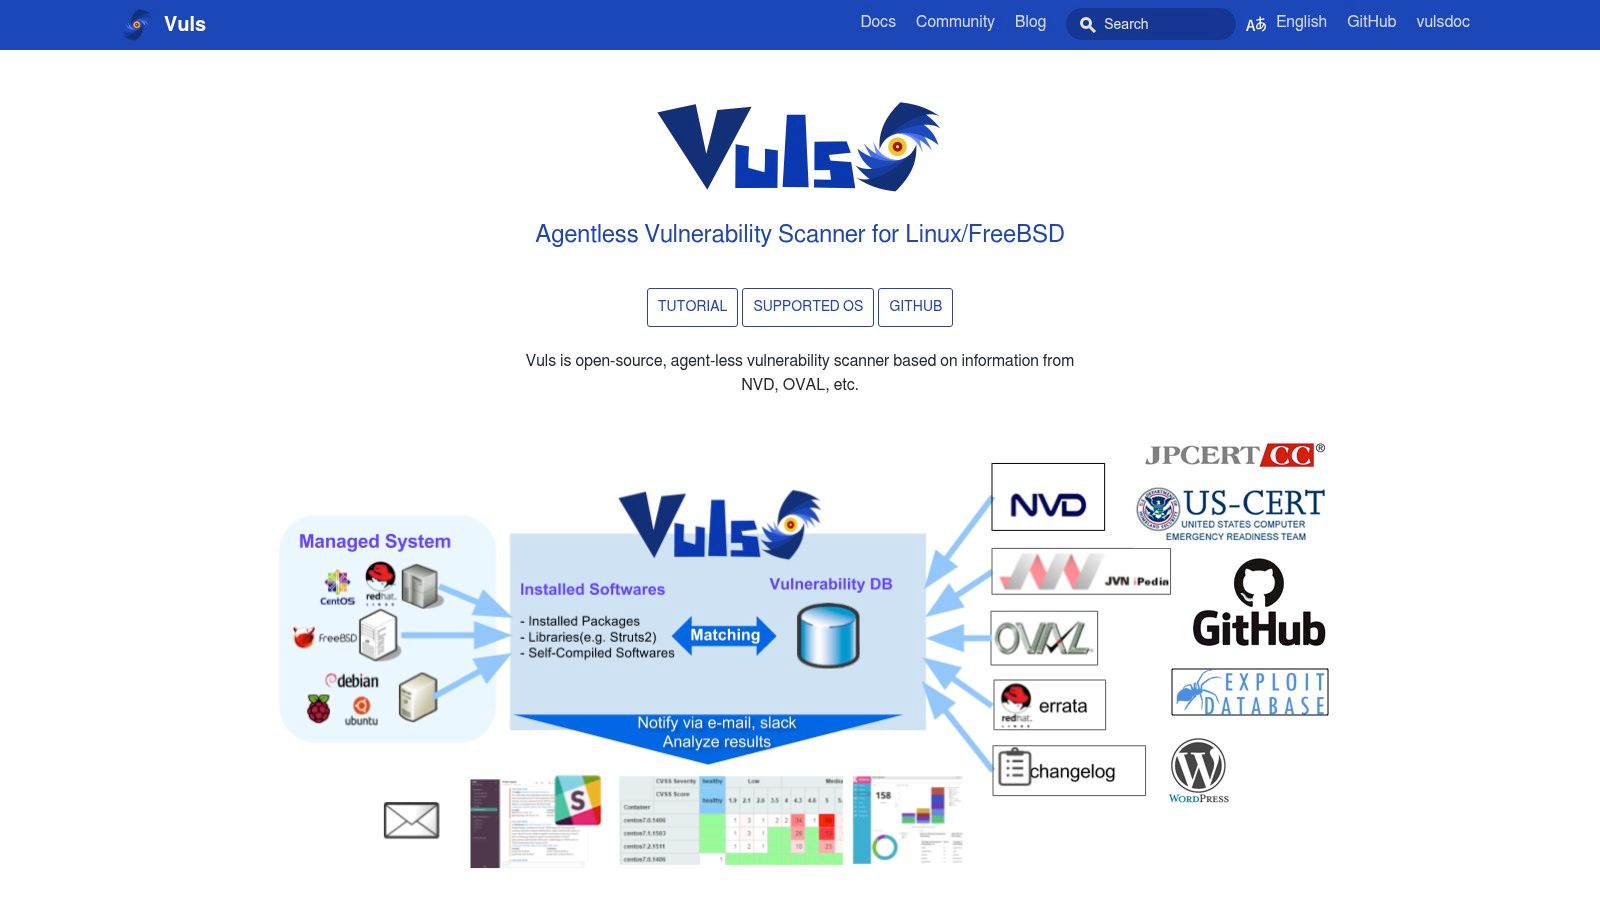
Top 10 Open-Source Vulnerability Scanners, Feature Comparison
| Product | Primary scope | Integration & automation | Target audience | Key strengths | Limitations / ops |
|---|---|---|---|---|---|
| Unified Security Stack Vulnerability Scanner | Network, endpoints, binaries (agent & network) | Deep SIEM/XDR & SOAR correlation, LLM-assisted triage, automated playbooks | Security teams / SOCs in hybrid enterprises | Contextualized findings, compliance mapping, open-source engines | Requires template tuning; agent rollout for deep scans |
| Greenbone Community Edition (OpenVAS/GVM) | Network & infrastructure vulnerability management | Web UI, APIs, scheduling; upgrade path to enterprise feeds | Network/security ops for routine infra scans | Mature NVTs, scheduler & reporting | Community feed has reduced coverage; paid feeds/appliances |
| OWASP ZAP (Zed Attack Proxy) | DAST for web apps & APIs | MITM proxy, headless CI modes, automation API | Appsec teams, developers, QA | Active/passive scans, fuzzing, large add-on ecosystem | Not for OS/container CVEs; active scans can disrupt targets |
| Nikto | Web server reconnaissance & baseline checks | CLI-friendly, scriptable outputs (XML/HTML/CSV) | Pen-testers, devs needing quick checks | Fast setup, low barrier for scripting | Signature-based, many findings need manual validation |
| OpenSCAP | Host vulnerability + compliance (SCAP/OVAL/XCCDF) | oscap CLI, SCAP Workbench, compliance profiles | Compliance teams & system administrators | Strong formal compliance mapping (PCI/CIS/STIG) | Effectiveness depends on up-to-date SCAP content |
| Lynis (CISOfy) | Host-based OS audit & hardening (Linux/macOS/Unix) | Lightweight scans, scripts, optional enterprise dashboard | Sysadmins, baseline hardening teams | Thorough OS checks, easy fleet baselining | Focused on OS hardening; enterprise features commercial |
| Trivy | Container images, filesystems, SBOMs, IaC, secrets | Fast DB updates, CI/CD & k8s integrations | Developers, CI/CD pipelines, SREs | Broad artifact coverage, quick startup | Enterprise governance & centralization are commercial |
| Grype (Anchore) | Container & filesystem CVE scanning; SBOM inputs | CLI + JSON outputs, tight SBOM workflows (Syft) | CI/CD engineers, container security teams | Strong SBOM integration, pipeline-friendly | Limited to package CVEs; advanced features commercial |
| Clair | Static container image analysis & indexing | API-first, registry/CI integration for server-side scans | Registry operators, platform teams | Proven registry integration, transparent matching | Static/package-focused; not a full DAST solution |
| Vuls | Agentless OS-level CVE detection (Linux/FreeBSD) | SSH/local scans, historical reports, VulsRepo viewer | Heterogeneous Linux/FreeBSD ops teams | No agent required, maps multiple advisory sources | Linux/FreeBSD only; does not cover Windows or apps |
Making Your Selection A Strategic Approach
Selecting the appropriate open-source scanner depends on the specific layer you need to cover. Greenbone/OpenVAS is strongest for network discovery and infrastructure assessment, OWASP ZAP for runtime web and API testing, Nikto for quick web server checks, OpenSCAP and Lynis for host compliance and hardening, and Trivy, Grype, Clair, and Vuls for checks at the container, package, artifact, and host levels. Unified Security Stack stands out because it does not halt at detection; it transforms scanner output into correlated security data that can drive response and compliance reporting.
The most frequent error is treating open-source scanners as interchangeable. They are not. The open-source sector has already fragmented into specialist tools, and the practical procurement question concerns coverage, not brand loyalty. If your stack spans networks, applications, containers, and compliance obligations, you will typically require more than one scanner, along with a centralized platform to normalize findings and eliminate duplicates.
This is where SIEM/XDR integration shifts the economics. Raw scanner output is inexpensive, but triage is costly. A vulnerability appearing in logs, asset inventories, and user activity is easier to prioritize than a generic CVE record, and this context enables teams to automate follow-up rather than manually chasing every finding. For regulated organizations, this same workflow also assists in converting scan evidence into audit-ready reporting for HIPAA, CMMC, and PCI.
Use the scanner that aligns with the layer you can maintain. Then, centralize the results. If you wish to see how an open-source platform can unify vulnerability scanning, correlation, and response in one place, visit Unified Security Stack and review how its vulnerability management and SIEM/XDR workflows integrate into a modern security program.
Unified Security Stack integrates vulnerability scanning, SIEM, SOAR, and XDR into a single open-source platform, which is precisely what teams require when scanner output accumulates faster than personnel can triage it. If you are comparing open-source vulnerability scanner tools, it can assist you in correlating findings with logs, assets, and compliance evidence rather than leaving them isolated in separate consoles. Visit Unified Security Stack to learn how such an integrated approach can streamline remediation and reporting.