Top 10 Vulnerability Management Tools for 2026
You likely confront the same challenge most security teams have in 2026. The scanner no longer represents the problem. The problem is determining what should be addressed first, who is responsible for remediation, and how all of it ties back to HIPAA, PCI, GLBA, ISO 27001, or CMMC evidence when an auditor arrives.
This explains why selecting vulnerability management tools has become harder rather than easier. The market is sizable, crowded, and continuing to expand. The broader vulnerability management market was valued at roughly USD 15.9 billion in 2023 and is expected to hit USD 34.7 billion by the end of 2032, with growth fueled by the increasing frequency and complexity of cyber threats, according to Global Market Insights. Buyers do not want yet another dashboard. They want integration, prioritization, and evidence that findings are actually remediated.
Operational pressure also plays a role. Over the past ten years, the average gap between disclosure and exploit activity has fallen from 45 days to 15 days, according to Gartner data cited by Recorded Future. That shifts the buying criteria. Continuous assessment, automation, and close integration with SIEM, XDR, ticketing, patching, and SOAR are no longer optional additions.
If you're comparing top vulnerability management solutions, the useful question is not which scanner detects the most CVEs. It is which platform matches my operating model. A CISO, an MSSP, a compliance officer, and a SOC lead will not evaluate the same tool in the same way.
Table of Contents
- 1. Unified Security Stack
- 2) Tenable Vulnerability Management
- 3. Qualys VMDR with TruRisk
- 4. Rapid7 InsightVM
- 5) Microsoft Defender Vulnerability Management
- 6) CrowdStrike Falcon Spotlight
- 7) Wiz Vulnerability Management
- 8. Orca Security
- 9) Ivanti Neurons for Risk-Based Vulnerability Management
- 10) ManageEngine Vulnerability Manager Plus
- Top 10 Vulnerability Management Tools Comparison
- From Data Overload to Strategic Risk Reduction
1. Unified Security Stack
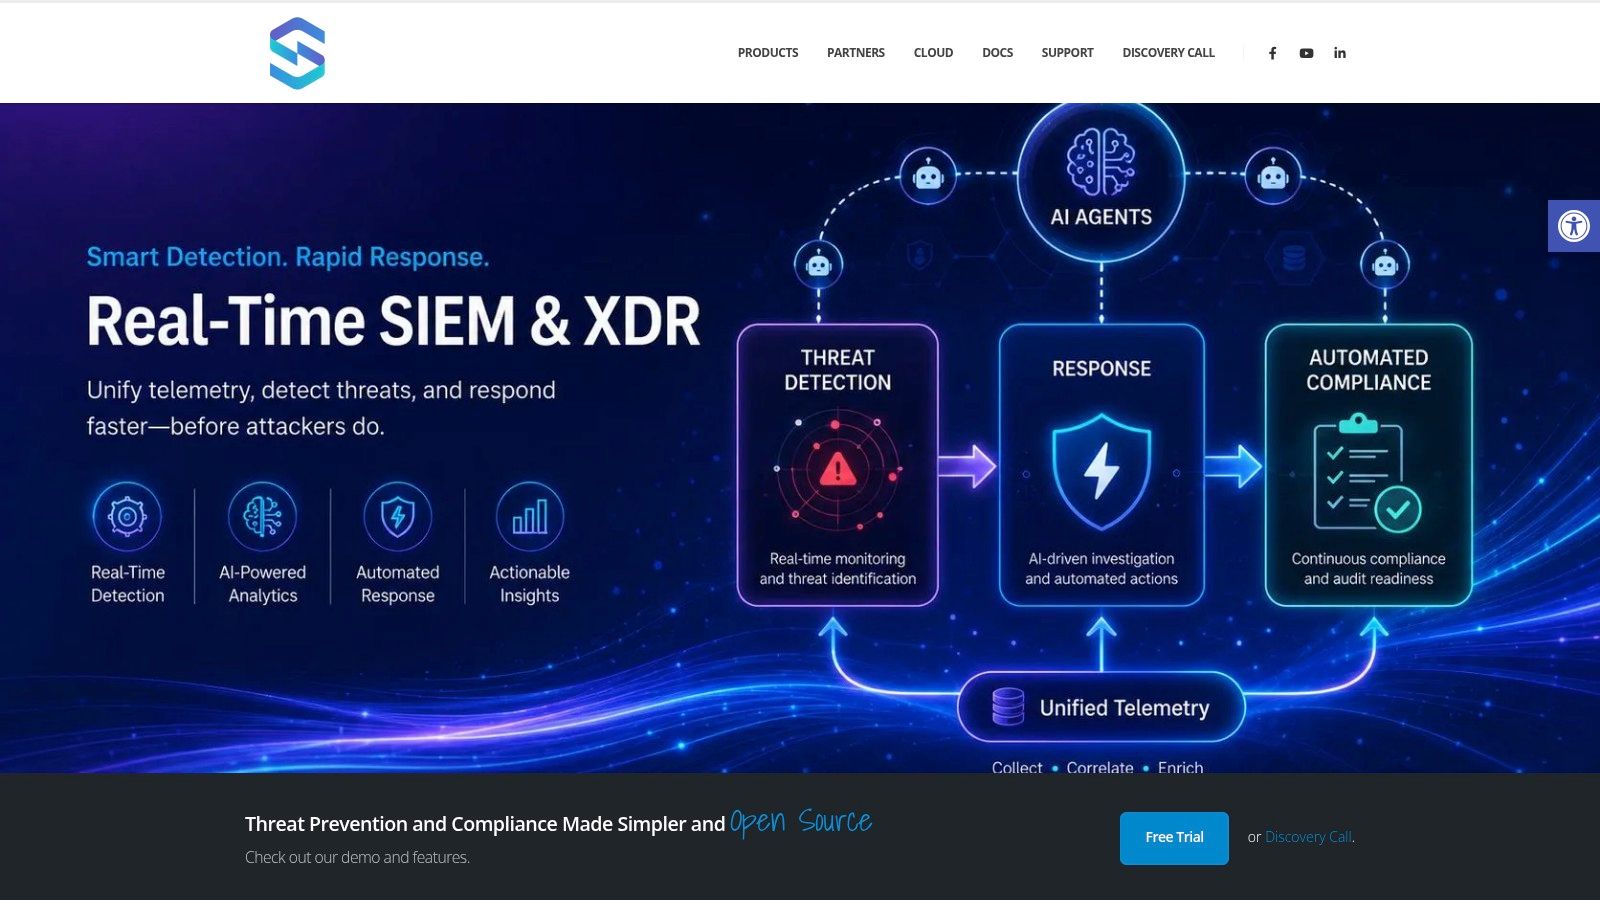
Unified Security Stack is the most compelling option on this list if you are tired of stitching together separate products for SIEM, SOAR, XDR, log management, vulnerability scanning, and compliance reporting. It is designed as a unified stack for hybrid environments, which matters because most remediation delays do not stem from missed detection. They stem from fragmented ownership across endpoint, cloud, network, and identity teams.
The architecture of Unified Security Stack is what sets it apart. Its correlation engine operates before indexing, which helps cut noise and manage indexing overhead while still enabling real-time detection and response. In practice, this alters analyst workflow. Teams spend less time sorting through duplicate alerts and more time pushing incidents into a response path that can be automated.
Why Unified Security Stack stands out
The modular stack encompasses log management, vulnerability scanning, access-rights auditing, endpoint protection/XDR, dark-web monitoring, and file tracking. Data ingestion supports APIs, Syslog, NetFlow, and agents, making it suitable for mixed environments instead of assuming all systems reside in a single cloud or on one endpoint platform. For a practical primer on scanner coverage, refer to Unified Security Stack's own overview of vulnerability scanning serves as a beneficial starting point.
Its compliance capabilities are stronger than those of many scanner-first tools. Built-in workflows align detections and evidence with CMMC, HIPAA, SOC 2, ISO 27001, PCI, GDPR, and GLBA. That matters to compliance officers who would rather not manually gather screenshots from five consoles each quarter.
Practical rule: If your team already operates a SIEM, creates tickets in a different platform, manages endpoint context somewhere else, and exports compliance evidence manually, a unified platform can eliminate more risk than upgrading a scanner.
A modern SOC usability benefit also exists. Integrated LLM features help with triage, rule tuning, and reducing false positives. That will not replace skilled analysts, but it can shorten the journey from raw finding to meaningful action.
Who should choose it
Unified Security Stack fits three personas especially well:
- CISOs in regulated sectors: Built-in compliance mapping helps convert detection and remediation activity into evidence for HIPAA, PCI, GLBA, ISO 27001, SOC 2, and CMMC.
- MSSPs and MSPs: The breadth of the platform supports multi-tenant service delivery more effectively than point products that need a separate console for every function.
- Security architects: It is a strong choice when the main requirement is integration across SIEM, SOAR, XDR, and vulnerability management, rather than just another scanner.
The trade-off is clear. Powerful open-source platforms require tuning, operational ownership, and personnel who understand detection engineering and workflow design. Unified Security Stack also does not publish public pricing, so buyers need a demo, trial, or sales conversation to understand support and deployment costs. Even so, if you want vulnerability management tools that operate inside a broader detection and response architecture rather than alongside it, Unified Security Stack merits serious consideration.
2) Tenable Vulnerability Management
Tenable Vulnerability Management is the conservative enterprise option, and that is not a criticism. Many teams want mature scanning, familiar workflows, and broad ecosystem support. Tenable provides that, especially for organizations that already trust the Nessus lineage.
That heritage also carries weight in the market. Nessus has a 68% adoption lead among global businesses, according to Business Research Insights. That does not automatically make Tenable the best fit for every environment, but it does explain why so many enterprises use it as the baseline against which everything else is measured.
Where it fits best
Tenable performs well in heterogeneous environments that require continuous assessment across servers, endpoints, and network devices without committing entirely to one endpoint vendor or one cloud-native architecture. Its dashboards, analytics, and APIs make it practical for teams that need integration with ITSM, SIEM, and SOAR. If you are comparing established scanners more broadly, this roundup of vulnerability scanning tools is a useful companion.
For CISOs, predictability is the draw. Tenable is simple to defend in procurement meetings because most buyers and auditors know the brand already. For security operations teams, the advantage is mature coverage and documented integration paths.
The downsides are familiar too:
- Pricing is quote-based: Budget planning requires vendor involvement.
- The UI can feel dense: Complexity often builds up in mature platforms over time.
- Remediation still depends on your surrounding stack: Discovery is robust, but operational closure typically requires ticketing, patching, and ownership discipline outside the scanner.
Tenable is a good match when you want a mature vulnerability management platform that won't surprise experienced operators. It is less persuasive if your core pain point is end-to-end remediation orchestration rather than scanning depth.
3. Qualys VMDR with TruRisk
Qualys VMDR with TruRisk typically comes up when a security program has already outgrown point scanners. A frequent scenario is a global enterprise with internet-facing assets, roaming endpoints, cloud workloads, and audit pressure from multiple directions at once. In that setting, Qualys appeals to teams that want asset discovery, vulnerability assessment, prioritization, and response joined in a single platform.
Qualys is at its best when asset inventory accuracy matters as much as raw scan coverage. If the CMDB is stale or business units deploy systems outside normal change control, VMDR gives security teams a way to find what exists first and debate ownership second. That alters the conversation for CISOs, because board reporting becomes less about total findings and more about whether the organization can trust its exposure picture.
TruRisk is part of that attraction. It lets teams rank findings beyond base severity, which helps when patch windows are limited and every queue is already overloaded. Compliance officers also gain value here, since the same platform can support control evidence, exception tracking, and audit-oriented reporting without forcing exports into three other tools.
The operational trade-off is genuine. Qualys covers a great deal, but breadth creates administration overhead. Teams still need to tune asset tagging, scanner placement, exclusions, and remediation workflows, or they end up with a large backlog that is technically prioritized yet still hard to action.
For MSSPs, Qualys can perform well in multi-client programs requiring consistent assessment and reporting across varied environments. Integration discipline is the challenge. When the service model relies on feeding prioritized findings into a SIEM, SOAR, or ticketing stack, value stems from how smoothly Qualys fits that workflow, not from scan data on its own. This is another area where unified platforms like Unified Security Stack can be significant. They provide operators with a way to correlate vulnerability context with detections, asset telemetry, and response activity rather than treating VM as a distinct reporting track.
Qualys is a solid choice for enterprises that want one platform to support exposure management, remediation coordination, and compliance reporting at scale. It is less appealing for teams that want lightweight deployment, simple packaging, or quick time to value with minimal tuning.
4. Rapid7 InsightVM
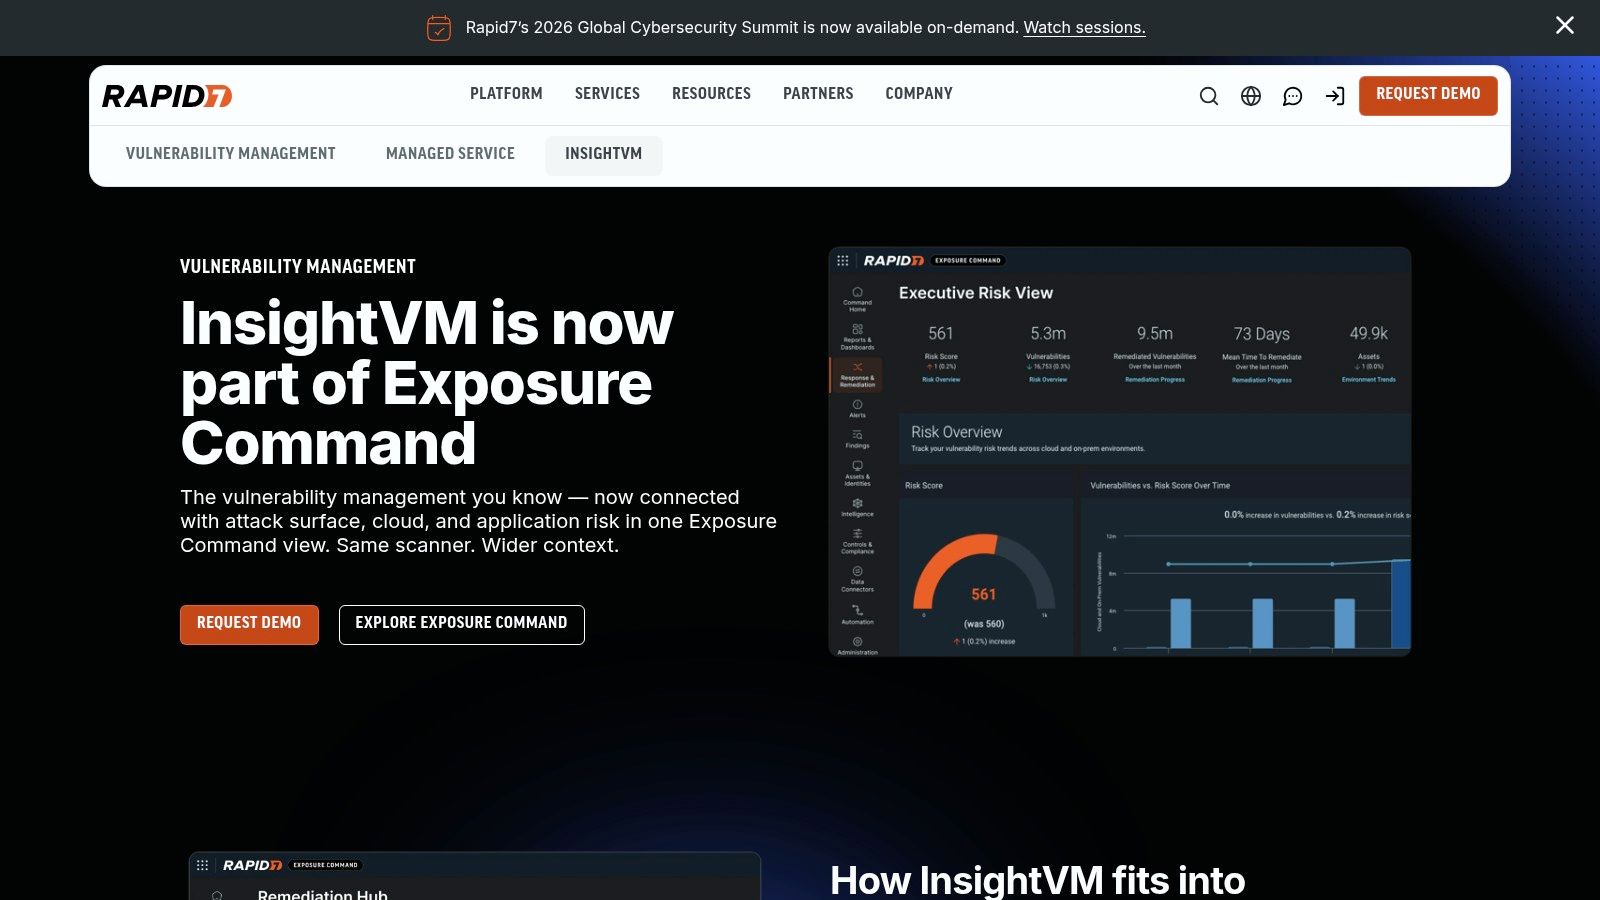
Rapid7 InsightVM Its value peaks when the security team prioritizes resolving findings as much as gathering them. Rapid7 has held an edge here for a long time. The offering centers on real-time dashboards, remediation projects, and connections to wider operational workflows instead of viewing scanning as the end point.
Visibility is not always the industry's biggest shortcoming; execution is. A frequently ignored fact in today's vulnerability management is the remediation black hole. Companies often find it hard to go from alert to patch since ownership, ticketing, verification, and closure are divided among too many systems, as discussed by CyCognito.
Best fit for remediation-driven teams
InsightVM is a strong match for teams that already use Jira, ITSM queues, and cross-functional remediation sprints. Its integration with Metasploit intelligence and internet telemetry adds useful context, but an important differentiator is how naturally it supports dialogue between security and infrastructure teams.
Rapid7 is often simpler to trial than many enterprise competitors that sell only through quotes. This matters to mid-market buyers and MSSPs that are testing a service offering before committing to a standard.
A few trade-offs show up in real deployments:
- Remediation workflows can still get messy at scale: Tools help, yet ownership discipline still counts.
- It's strongest when paired with the wider Insight platform: Buyers can gain additional value when they already rely on related Rapid7 products.
- Segmented networks still require planning: On-premises scan engines address that problem, although they add architectural effort.
Security leaders who want vulnerability management tools to support genuine remediation programs rather than produce static reports often shortlist InsightVM, and for good reason.
5) Microsoft Defender Vulnerability Management
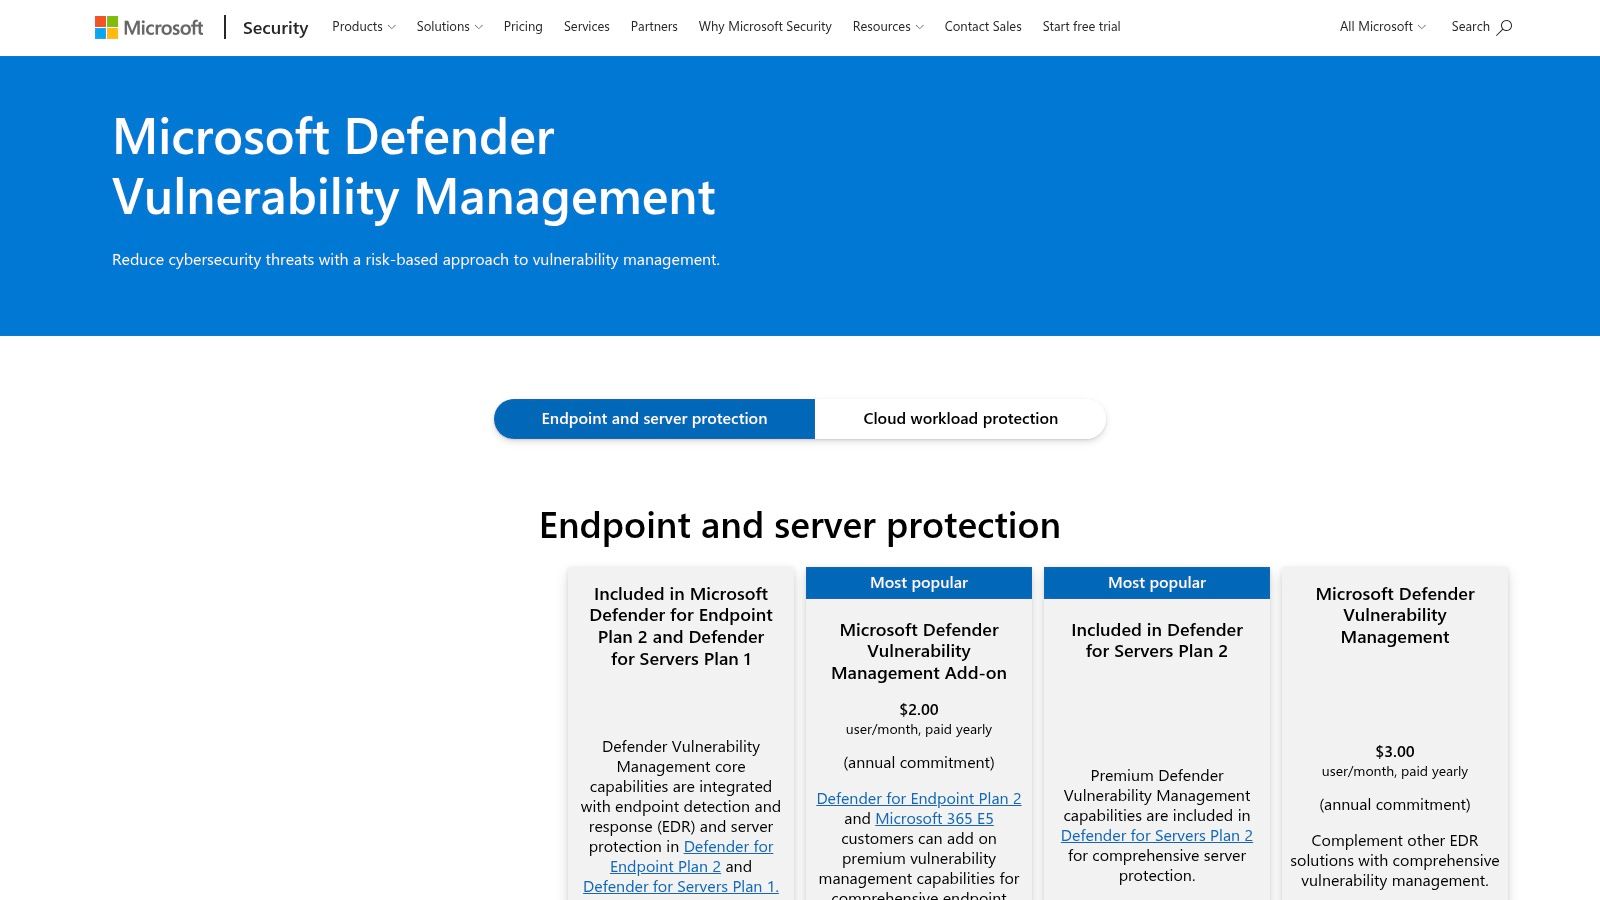
A typical situation looks like this. The SOC already operates in Microsoft Defender XDR, identity teams reside in Entra, and endpoint operations rely on Defender for Endpoint. In that environment, Microsoft Defender Vulnerability Management usually prevails because it brings exposure visibility into tools the team already uses, rather than requiring another console, another agent, and another integration project.
This matters to various buyers for various reasons. CISOs gain closer alignment among vulnerability data, endpoint telemetry, and identity context. Compliance officers gain a clearer route to demonstrate remediation status for managed assets. MSSPs can use it effectively for Microsoft-heavy clients, but they must also be candid about tenant boundaries, reporting expectations, and how much of the customer estate sits within the Microsoft stack.
Best fit for Microsoft-first security programs
MDVM performs best when the endpoint estate already has Microsoft security controls instrumented. Security teams can prioritize weaknesses through device exposure data, view relevant recommendations in the same administrative plane as incident investigation, and pass remediation tasks to endpoint teams without creating a separate scanner workflow from the beginning.
The compromise is coverage depth beyond that ecosystem.
- Best visibility comes from Microsoft-controlled telemetry: The cleanest fit comes with Windows and Microsoft-managed endpoints.
- Heterogeneous environments need extra design work: Linux, macOS, network appliances, cloud-native assets, and third-party applications might call for additional tools or changes to process.
- Service providers need to plan around operations, not just features: Platforms designed to aggregate across a broad estate make multi-tenant reporting and cross-client standardization simpler; this includes unified approaches like Unified Security Stack.
MDVM performs well within an XDR-led operating model. It is less compelling as the sole vulnerability management layer for organizations with extensive non-Microsoft estates. Yet for teams already invested in Microsoft security, it can lower friction, sharpen analyst context, and keep remediation conversations nearer to the systems where security and IT already operate.
6) CrowdStrike Falcon Spotlight
A frequent situation unfolds this way. The SOC already has Falcon deployed across thousands of endpoints, the CISO wants vulnerability data linked to active threat activity, and the IT team does not want to launch another scanning initiative that would trigger debates over credentials, scheduling, and ownership.
CrowdStrike Falcon Spotlight is a strong match for that environment. It relies on the Falcon sensor to continuously assess software exposure, keeping vulnerability triage within the same console that many analysts already use for detection and response.
This counts for more than convenience alone. For a CISO, Spotlight can cut tooling sprawl and keep exposure reporting nearer to operational reality on managed endpoints. For MSSPs, it delivers the most value in customer estates already standardized on Falcon, since analyst workflow, telemetry, and response actions remain within one vendor stack. For compliance officers, the benefit is narrower unless the organization can also demonstrate remediation ownership and exception handling beyond the Falcon interface.
Best fit for endpoint-led security operations
Spotlight performs best in programs where endpoint telemetry serves as the primary source of truth. Analysts can view vulnerable software alongside host activity, device posture, and threat signals, rather than reading a separate scanner report that lacks endpoint context.
The trade-off is scope.
Spotlight is less compelling as the sole vulnerability management layer for organizations requiring broad coverage across network devices, unmanaged assets, operational technology, or cloud-native workloads. It can reveal a great deal about systems where the Falcon agent is installed. It says much less about assets that never entered the agent deployment plan to begin with. That shortfall matters to compliance teams and service providers that need estate-wide reporting, not only strong endpoint visibility.
Architect's note: Assessment without scans lowers operational overhead, yet patch ownership, maintenance windows, compensating controls, and exception reviews still decide whether risk truly declines.
From a commercial standpoint, Spotlight is most sensible as part of a larger Falcon purchase. Teams already using Falcon for EDR or XDR typically have a stronger justification, since the integration value is immediate. Teams considering it as a standalone product should weigh that convenience against platforms designed to aggregate findings across mixed tools and tenants, including unified approaches such as Unified Security Stack.
When Falcon already sits at the center of security operations, Spotlight is a sensible add-on. When the estate is highly heterogeneous, it tends to be one part of the program rather than the entire solution.
7) Wiz Vulnerability Management
Wiz Vulnerability Management is not trying to be a conventional scanner with cloud support. It is a cloud-native risk platform where vulnerability management is one component of a broader graph-based exposure model. That distinction is important.
For cloud teams, the more useful question often is not whether this workload has a CVE. It is whether this vulnerable workload connects to sensitive data, privileged identities, exposed services, or a realistic attack path. Wiz is highly effective at answering that.
Cloud context is the real product
Wiz fits cloud-first organizations that require fast onboarding across AWS, Azure, and GCP. An agentless-first deployment brings teams to visibility rapidly, and the graph-based model helps prioritize what matters across sprawling cloud estates.
This approach to prioritization matters more and more because identity context alters vulnerability severity in real-world practice. A host with a moderate software flaw can become urgent if it also lies on a path to privileged roles or lateral movement. That identity-vulnerability blind spot ranks among the largest gaps in mainstream vulnerability management, as discussed by Vectra AI.
Wiz is especially good for:
- Cloud security leaders: Solid context for analyzing attack paths and blast radius.
- DevSecOps teams: Quick setup without extensive agent deployments.
- CISOs with cloud-heavy estates: Stronger board-level narratives about exposure than a raw CVE list.
The trade-off concerns scope. Hybrid and on-prem coverage frequently require additional components or a second product. Wiz excels in cloud environments, yet it is not a complete substitute for every traditional enterprise scanning requirement.
8. Orca Security
Orca Security appeals to teams seeking cloud vulnerability management with minimal deployment friction. Agentless coverage across cloud workloads, containers, data stores, and posture issues makes it appealing for organizations that do not want another large-scale endpoint rollout merely to gain visibility.
The strength of the product lies in context. Orca does not merely enumerate vulnerabilities. It aims to show how findings intersect with exposure, privilege, and reachable paths across the cloud estate.
Best for cloud teams that want low friction
This context-first approach matches the direction of vulnerability management. In 2026, effective tools require threat intelligence to rank risks by severity, ensuring critical threats come first rather than being handled only by scan volume or schedule, according to Swimlane.
Orca suits organizations that need cloud coverage quickly, particularly when the security team has little appetite for lengthy deployment projects. It is also helpful for compliance teams seeking posture and vulnerability evidence within one cloud security workflow.
The trade-offs are easy to state:
- Cloud-first by design: On-prem infrastructure typically calls for a different approach.
- Quote-based pricing: Buying requires a discussion.
- Best value comes from cloud concentration: Where your environment is more traditional, the fit is correspondingly less complete.
When public cloud workloads and identities hold your greatest risk concentration, Orca offers one of the clearer routes to fast visibility without agent proliferation.
9) Ivanti Neurons for Risk-Based Vulnerability Management
Ivanti Neurons for Risk-Based Vulnerability Management fits settings where vulnerability management is as much an integration challenge as a detection one. Organizations with several scanners, tools inherited through acquisitions, or distinct IT and security teams frequently require a system that can normalize findings and direct action to the appropriate operational owner.
This distinction varies by persona. A CISO typically wants a single defensible risk view rather than three competing dashboards. A compliance officer needs proof that findings were tracked through remediation, not merely discovered. An MSSP needs consistency across tenants without requiring every customer to use the same scanner stack.
Strong fit for fragmented programs that need workflow discipline
Ivanti's value lies less in raw discovery and more in unifying data, prioritization, and remediation workflows. The platform grows more useful when linked to Ivanti patching, endpoint management, or service management processes, since a vulnerability can then progress from finding to ticket to fix within one connected operating model.
That is the real-world compromise.
Teams already using Ivanti in adjacent functions can gain meaningful efficiency from that linkage. Teams seeking a lightweight scanner with simple packaging and minimal architecture effort may find it heavier than necessary. In a modern SIEM, XDR, and SOAR environment, Ivanti is typically best positioned as the system that turns fragmented scanner output into action, while a platform such as Unified Security Stack can remain the broader analytics and response layer across security telemetry.
Its trade-offs are straightforward:
- Packaging often needs clarification: Purchasers should outline modules and licensing from the start.
- Operational alignment drives value: The product delivers its greatest value when IT operations will use the outputs.
- Internal positioning takes work: Ivanti's case rests on consolidation, workflow control, and remediation follow-through, not on flashy dashboards.
For mature programs seeking to lower handoff friction among security, IT, and compliance, Ivanti is a credible choice. For smaller teams or buyers prioritizing rollout speed, it may feel like more platform than product.
10) ManageEngine Vulnerability Manager Plus
A typical mid-market scenario is this: the security lead also manages endpoint tooling, patch coordination belongs to IT, and the compliance officer requires evidence that issues were identified and resolved on time. In that setting, ManageEngine Vulnerability Manager Plus makes sense because it keeps scanning, prioritization, and patching closely connected, rather than making a small team combine three separate products.
The main draw is that operating model.
For CISOs at smaller organizations, the benefit is easier execution. The platform is generally simpler to budget and pilot than larger enterprise suites, which matters when security must demonstrate progress this quarter rather than after a lengthy procurement and integration cycle. For compliance teams, the value is clear reporting and better remediation tracking. For MSSPs, the picture is more mixed. It can suit smaller customer environments, but it is usually not the first choice for providers requiring broad multi-tenant scale and deep cross-client workflow control.
The trade-off is evident. ManageEngine performs best when the program centers on endpoints and servers, and when the team wants a single product that can move from finding to fix with less architecture effort. It is less persuasive for organizations needing advanced cloud exposure analysis, identity-centric risk context, or the normalization layer that supports a larger detection and response program.
This is significant for today's security operations.
When a team already operates a SIEM, XDR, or SOAR stack, ManageEngine generally fits as the vulnerability and remediation engine rather than the central analytics layer. A unified platform such as Unified Security Stack can still offer the broader correlation point across logs, alerts, and response workflows, while ManageEngine manages daily vulnerability operations for lean internal teams.
Its practical limits are easy to understand:
- Good fit for budget-conscious teams: Pricing and packaging tend to be simpler to justify internally.
- Best in IT-led security programs: It performs well where endpoint administration and patch ownership are already close to security.
- Less suited to cloud-first exposure management: Buyers with substantial cloud, container, or identity risk demands may outgrow it.
For SMBs and mid-sized organizations seeking a product their teams will actually deploy, maintain, and use, ManageEngine is a dependable option. It is not the widest platform here, yet it frequently fits staffing realities better than tools built for far larger security programs.
Top 10 Vulnerability Management Tools Comparison
| Product | Focus / Coverage | Core features & unique selling points | Target audience | Pricing & licensing |
|---|---|---|---|---|
| Unified Security Stack | Unified SIEM + SOAR + XDR for hybrid environments | Pre-ingest correlation; LLM-assisted triage; modular stack (logs, vuln scan, XDR, access audit, dark-web, file tracking); 30B+ IOC elements | Regulated orgs and teams seeking an open-source, extensible unified security platform | Open-source / Linux Foundation backed; free trial/discovery call; no public list pricing |
| Tenable Vulnerability Management | Cloud VM for on‑prem, cloud & hybrid assets | Continuous assessment; Nessus research heritage; rich dashboards & APIs | Enterprises standardizing on established VM vendors | Quote-based (no public pricing) |
| Qualys VMDR with TruRisk | End‑to‑end VMDR (discovery → remediation) | TruRisk prioritization; optional patch orchestration; unlimited virtual scanners/agents; strong compliance reporting | Large enterprises with broad estates and compliance needs | Quote-based; complex bundles |
| Rapid7 InsightVM | Cloud‑managed VM with exploit intelligence | Live dashboards & remediation projects; Metasploit telemetry integration; APIs; on‑prem scan engines | Teams valuing easy pilot/scale and Insight platform integration | Entry pricing advertised; scales to enterprise (contact sales) |
| Microsoft Defender Vulnerability Management | Endpoint‑centric VM integrated with Microsoft stack | Built‑in exposure assessment; Microsoft security benchmark reporting; native endpoint/identity integration | Organizations standardized on Microsoft 365/Defender | Included or add‑on within Microsoft licensing (E5/Defender suites); public guidance via MS docs |
| CrowdStrike Falcon Spotlight | Sensor‑driven, scan‑less VM using Falcon telemetry | Continuous real‑time visibility; ExPRT prioritization; rich endpoint context; APIs | Existing CrowdStrike Falcon customers wanting low overhead | Quote-based; typically sold as a Falcon module |
| Wiz Vulnerability Management (CNAPP) | Agentless‑first cloud VM across AWS/Azure/GCP | Agentless discovery; graph‑based risk & attack‑path analysis; broad cloud vulnerability coverage | Cloud‑native orgs seeking fast onboarding and contextual cloud risk | Quote-based; available via cloud marketplaces |
| Orca Security | Agentless cloud security and VM | Agentless scanning; unified risk graph; contextual risk scoring and compliance reporting | Teams needing rapid, low‑friction multi‑cloud visibility | Quote-based (no public pricing) |
| Ivanti Neurons RBVM | Risk‑based VM that aggregates scanners | Vulnerability Risk Score (VRS); consolidates multiple scanner feeds; patch orchestration integrations | Organizations wanting consolidated risk views and automated remediation workflows | Quote-based; packaging varies by bundle |
| ManageEngine Vulnerability Manager Plus | SMB / mid‑market all‑in‑one VM + patching | Built‑in patch management; 850+ third‑party app coverage; clear edition comparison; free edition available | SMBs and resource‑constrained IT/security teams | Transparent tiered pricing and public SKUs; free edition available |
From Data Overload to Strategic Risk Reduction
After each large scan cycle, the same situation tends to repeat. The dashboard is crowded, exposures remain elevated, and each group raises its own concern. The CISO asks which issues could become business risk this quarter. The compliance officer looks for proof that control gaps are monitored and resolved. The MSSP needs to triage across tenants without overwhelming analysts with repeated tasks. The architect questions whether the tool can send data into SIEM, XDR, SOAR, ticketing, and patch processes without creating another fragile integration effort.
That is the benchmark that counts in 2026. Vulnerability management tools are no longer assessed solely on how deeply they detect. Experienced buyers focus on prioritization accuracy, how ownership is routed, verification of remediation, and whether the platform can generate reporting that serves executives, auditors, and operations simultaneously.
Evaluating by persona highlights product distinctions more clearly. A CISO generally requires risk perspectives that lower noise and enable board-level reporting. A compliance officer requires evidence tied to frameworks such as PCI-DSS, SOC 2, ISO 27001, HIPAA, and GDPR, ideally without moving raw findings into spreadsheets. An MSSP requires tenant isolation, repeatable processes, and role controls that remain reliable across many customers. A security architect requires stable APIs, asset context, and integration routes that link vulnerabilities to identity, endpoint, cloud, and network telemetry. AccuKnox makes a comparable point in its review of vulnerability management tools.
Tool choice also reflects where operational focus already resides. Teams with mature standalone programs may find the greatest benefit in Tenable, Qualys, or Rapid7, since those products enable deeper VM-specific workflows and extensive scanner coverage. Organizations standardized on Microsoft or CrowdStrike often move faster by remaining in that ecosystem, even if certain reporting or workflow capabilities involve licensing and platform trade-offs. Cloud-centric teams typically obtain stronger context from Wiz or Orca, because asset relationships, exposure paths, and cloud misconfigurations carry as much weight as CVE counts. Smaller IT and security teams may be better supported by ManageEngine when they need patching and vulnerability management combined in one maintainable package.
A unified operating approach counts for more than the sheer number of features.
Within that model, Unified Security Stack is relevant because it embeds vulnerability management in a wider SIEM, XDR, and SOAR workflow rather than presenting it as a standalone console. This alters how findings are processed. A high-risk exposure can be linked with endpoint activity, identity events, network telemetry, and compliance status before it arrives in an analyst queue. For a CISO, this strengthens risk communication. For a compliance officer, it reduces the distance between finding and evidence. For an MSSP, it can cut context switching and streamline cross-client operations, provided the multi-tenant controls align with the service model.
The most effective programs create a repeatable sequence: identify the issue, assign an owner, verify remediation, and retain evidence. This may sound straightforward, yet it is where many deployments get stuck. The wrong tool introduces handoffs among security, IT, cloud, and compliance that no one clearly owns. The right tool matches how those teams already operate, or offers them a practical way to improve without reconstructing the entire operating model.
Select the platform your teams can integrate, operate, and defend during an audit or incident. A product that appears strong in a feature matrix still falls short if its connectors are weak, its workflows do not align with your owners, or its reporting fails as soon as an executive poses a more difficult question.