Top Five Free and Open Source SIEM
As cybersecurity becomes increasingly critical, organizations need to remain alert when safeguarding digital assets and sensitive data. Security Information and Event Management (SIEM) solutions play a vital role here, offering broad insight into an organization’s security posture. Although numerous commercial SIEM tools exist, interest in genuinely free and open-source SIEM options continues to grow.
One benefit of open-source SIEM solutions is transparency: organizations can inspect the source code for possible security weaknesses and adapt the software to meet their needs. Still, open-source SIEM solutions differ in quality. This article examines the top 5 genuinely free and open-source SIEM tools that can help strengthen an organization’s cybersecurity defenses.
1. UTMStack SIEM
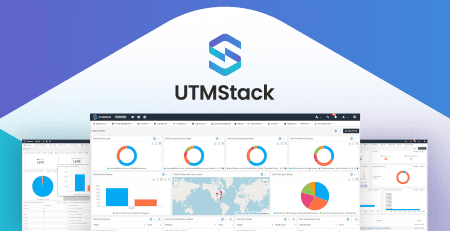
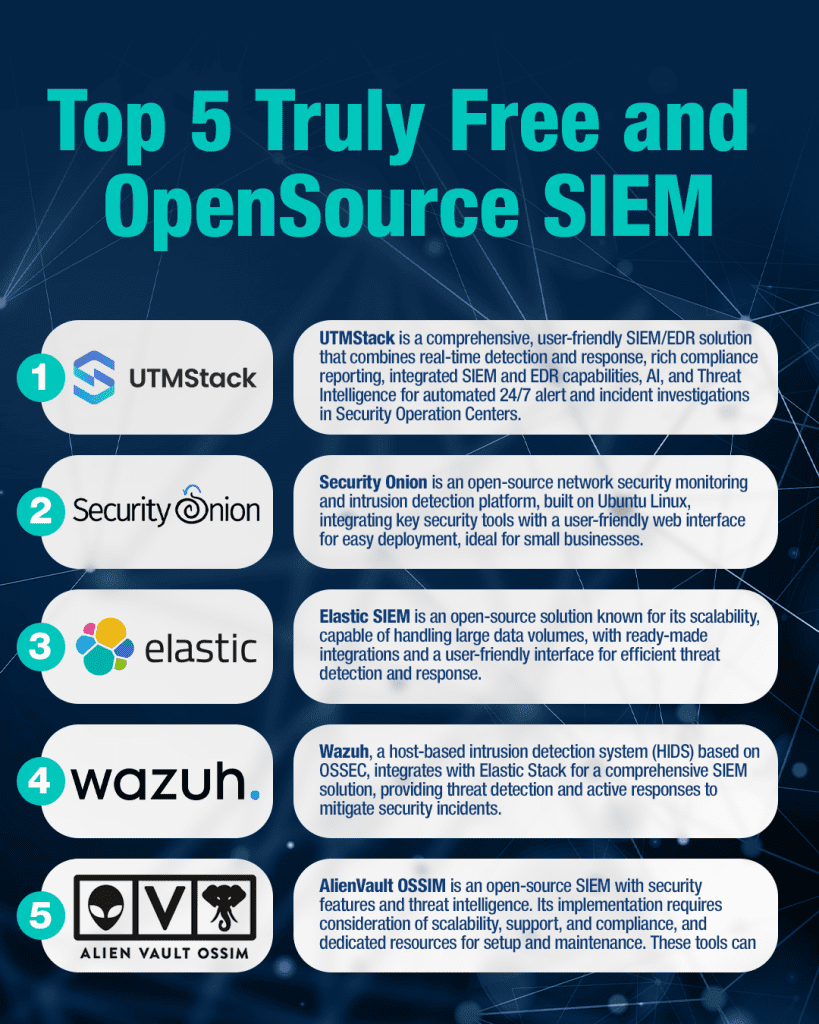
Unified Security Stack is a free and open-source SIEM/EDR that provides real-time detection and response. It displays alert and log data through an intuitive interface with extensive compliance reporting. This novel method combines SIEM and EDR capabilities with Threat Intelligence and AI to help Security Operation Centers conduct automated alert and incident investigations around the clock.
2. Security Onion:
Security Onion is a well-known open-source platform for network security monitoring and intrusion detection. It runs on the widely used Ubuntu Linux distribution and brings together several essential open-source security tools, including Suricata, Snort, Zeek (formerly Bro), and Elastic Stack components. Security Onion’s web-based management interface streamlines deployment and configuration, making it a strong option for both small businesses seeking a simple
3. Elastic SIEM
Elastic SIEM, comprising Elasticsearch, Logstash, and Kibana, is a robust open-source SIEM solution recognized for scalability and flexibility. It is able to ingest, store, and analyze high volumes of data, which makes it well suited to enterprises with large amounts of log data. Elastic Stack also provides prebuilt SIEM integrations and an intuitive interface for effective threat detection and incident response.
4. Wazuh SIEM:
Wazuh is a host-based intrusion detection system (HIDS) derived from OSSEC that can be combined with Elastic Stack to form a comprehensive SIEM solution. Wazuh delivers threat detection and active responses to reduce security incidents.
5. AlienVault OSSIM:
AlienVault OSSIM is an open-source security information and event management system built for straightforward setup and use. It includes many built-in security plugins and correlation rules for detecting threats. AlienVault OSSIM also connects with the Open Threat Exchange (OTX), which offers access to extensive threat intelligence.
Before deploying an open-source SIEM solution, organizations should evaluate factors including scalability, integration ease, and community support. In addition, it is essential to confirm that the solution fits your particular compliance and regulatory requirements.
Although these genuinely free and open-source SIEM solutions provide an economical means of strengthening your organization’s cybersecurity, remember that they may need dedicated resources for setup, maintenance, and continued support. The open-source community can be a significant asset, and with proper expertise, these SIEM solutions can serve as strong allies against cyber threats.
In a world where the threat landscape keeps changing, these top 5 genuinely free and open-source SIEM solutions can help organizations remain one step ahead of possible cyber adversaries. With the right SIEM tool deployed, you can protect your data, secure your systems, and support your business’s continued success in the digital age.